
DCE-210 · Lesson 4 of 12 · 29 min
Virtual networks, security and network services
A data centre network does more than move packets between racks. A cloud or colocation provider must give each customer a private network that behaves as if it were the only one, keep customers and systems isolated from each other, spread incoming requests across many servers, absorb attacks from the internet, and encrypt traffic that crosses shared infrastructure. This lesson describes the virtual networks and network services that sit on top of the physical fabric from Lesson 3, and the security principles that guide them.
Multi-tenancy: many networks on one fabric
A tenant is a customer, department or application that needs its own isolated network. Isolation is built in layers:
- VLANs separate layer 2 segments on a switch, but are limited to 4094 per domain and do not extend well across a routed fabric.
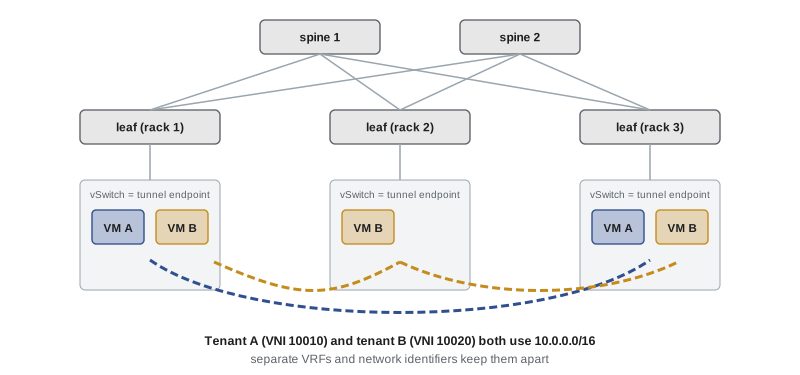
- VRFs (virtual routing and forwarding instances) give each tenant its own routing table on the same router or switch, so two tenants can even use the same private addresses without conflict.
- Overlays such as EVPN-VXLAN (Lesson 3) carry each tenant's traffic in tunnels identified by a 24-bit network identifier across the shared underlay, giving over 16 million segments.
- In public clouds, the overlay usually starts in software on the server itself rather than on the leaf switch. Each customer sees a virtual private cloud (VPC) with its own address space, subnets, route tables and gateways, all implemented by the provider's host networking stack.
Networking inside the server
A server hosting virtual machines or containers contains a network of its own. A virtual switch, such as Open vSwitch or the Linux kernel bridge, connects the virtual interfaces of the guests to the physical network card and applies the tenant's overlay, security rules and policies. Doing this in software costs CPU cycles: at 100 Gb/s and above, packet processing could consume many processor cores that the provider would rather rent to customers.
The response has been to move networking into hardware on the network card:
- SR-IOV (single-root I/O virtualization) lets one physical card present many virtual functions that are assigned directly to guests, bypassing the software switch.
- SmartNICs and DPUs (data processing units) are network cards with their own processors and programmable packet engines. They run the virtual switch, overlay, firewall, encryption and storage protocols on the card, isolating them from the host. Amazon's Nitro cards, NVIDIA BlueField and AMD Pensando are examples.
For the facility this means more of the "network" lives inside servers, and network cards may draw 50 W to 150 W each, which adds to the rack power budget.
Load balancing
Popular services run on many identical servers. A load balancer presents one address to clients and spreads their connections across the servers behind it, checking each server's health and removing failed ones.
- Layer 4 load balancers decide using IP addresses and ports. They are fast and simple and can handle millions of connections per second.
- Layer 7 load balancers terminate the client connection, read the HTTP request and route by URL, header or cookie. They can also terminate TLS, compress responses, cache content and apply web application firewall rules.
- Health checks probe each server every few seconds and remove it from service after repeated failures.
- Algorithms include round robin, least connections, weighted distribution and hashing on the client address so that each client keeps returning to the same server.
Large operators avoid dedicated load-balancer appliances as a single choke point. Instead they announce the service address from many servers or load-balancer instances at once and let the fabric's ECMP hashing (Lesson 2) spread the flows, a technique called anycast or ECMP load balancing. Responses can also bypass the load balancer entirely (direct server return), because responses are usually much larger than requests.
Worked problem
Why consistent hashing
A load balancer assigns clients to 10 cache servers using "hash modulo 10". An eleventh server is added and the rule becomes "hash modulo 11". What fraction of clients move to a different server? What fraction would move with consistent hashing?
Show solution
- With modulo hashing, a client stays put only if its hash gives the same remainder for 10 and 11, which happens for about 1 in 11 clients. About 10/11 move.
- Consistent hashing places servers and clients on a ring; adding one server takes over only the share it now owns, about 1/11 of clients.
Answer: About 91% of clients move with modulo hashing, emptying almost every cache at once, but only about 9% with consistent hashing. Load balancers and distributed caches use consistent hashing (or variants such as Maglev hashing) so that adding or losing a server disturbs as little as possible.
Security principles
A data centre network carries the most valuable data an organization has, and attackers who get inside one system try to move laterally to others. Network security in a data centre rests on a few principles:
- Defence in depth: no single control is trusted to stop every attack. Physical security, network segmentation, host hardening, identity, encryption and monitoring overlap.
- Least privilege: each system can reach only what it needs. A web server can reach its application servers on one port, not the backup network or the building management system.
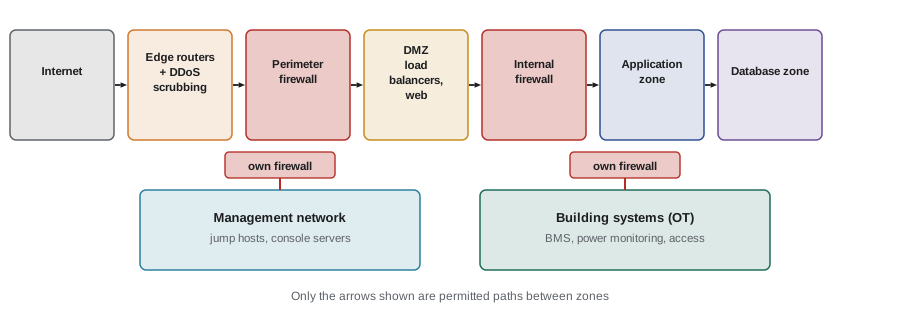
- Segmentation: networks are divided into zones (internet-facing, application, database, management, building systems) with controlled paths between them. Microsegmentation applies rules to each workload individually, usually in the host or DPU, so that two servers in the same rack cannot talk unless allowed.
- Zero trust: no device or user is trusted just because it is inside the network. Every connection is authenticated and authorized, as described in NIST SP 800-207.
Firewalls
Firewalls enforce the rules between zones. Stateful firewalls track each connection and allow return traffic automatically; next-generation firewalls also identify applications, inspect content and block known threats. In a data centre, traffic between servers inside the building (east-west) far exceeds traffic to and from the outside (north-south), and sending all of it through central firewall appliances would create bottlenecks. Modern designs therefore filter north-south traffic at the perimeter with dedicated appliances and enforce east-west policy in a distributed way: access lists on leaf switches, security groups in the cloud, and host or DPU firewalls.
The management and building networks
Two networks deserve special care. The out-of-band management network connects to the console and management ports of switches, servers and power equipment, and lets engineers recover the production network when it fails; it should be physically separate, reachable only through hardened jump hosts with multi-factor authentication, and have its own internet or cellular access. The building systems network carries the building management system, electrical power monitoring, fire alarm interfaces and access control (DCE-200, Lesson 12). These operational technology (OT) systems are often old, hard to patch and critical to keeping the facility running, so they must be isolated from IT networks and from the internet, with any remote access tightly controlled.
In Canada, the Canadian Centre for Cyber Security publishes guidance for securing networks and operational technology, and many operators align with the NIST Cybersecurity Framework and ISO/IEC 27001. Privacy obligations for personal data held in data centres come from PIPEDA and provincial laws.
Distributed denial of service
A distributed denial-of-service (DDoS) attack floods a target with traffic from many compromised devices, often hundreds of thousands of hijacked cameras, routers and servers. Volumetric attacks aim to fill the target's links; protocol attacks exhaust state in firewalls and servers; application attacks send expensive requests that look legitimate. The largest volumetric attacks reported in 2025 exceeded 20 Tb/s for short periods, far more than any single data centre's internet capacity.
No data centre can absorb attacks of that size on its own links, so defences work upstream:
- Scrubbing services and large content delivery networks absorb attacks across their global capacity, filter malicious traffic and forward clean traffic to the customer.
- Remotely triggered blackholing asks upstream carriers to drop all traffic to an attacked address, sacrificing that one address to protect the rest.
- Rate limits, SYN cookies and application-layer filtering handle smaller attacks at the edge.
Worked problem
Sizing for an attack
A data centre has four 100 Gb/s transit links, normally carrying 120 Gb/s in total. A 1.2 Tb/s attack arrives, spread evenly across the links. What fraction of legitimate traffic gets through if nothing is done?
Show solution
- Capacity: \(4 \times 100 = 400\) Gb/s.
- Offered traffic: \(1200 + 120 = 1320\) Gb/s.
- If drops fall evenly on all traffic, the fraction delivered is \(400/1320 = 0.30\).
Answer: Only about 30% of legitimate traffic gets through, so the service is badly degraded. Even with perfect filtering at the data centre, the links themselves are full, which is why the attack must be absorbed upstream by a scrubbing service with terabits of capacity.
Encryption in the network
Traffic that crosses links outside the operator's physical control, such as dark fibre between buildings or a carrier's wavelength, can be tapped. Many operators now encrypt everything that leaves a building, and increasingly traffic inside it too:
- MACsec (IEEE 802.1AE) encrypts each Ethernet link at line rate in the switch or network card hardware. It adds 16 to 32 bytes per frame (a security tag of 8 to 16 bytes and an integrity check value of 16 bytes).
- IPsec encrypts IP packets between gateways or hosts and is common for site-to-site VPNs across the internet.
- TLS encrypts individual application connections and is used by almost all web traffic and, increasingly, by traffic between services inside a data centre (often with mutual authentication in a service mesh).
- Optical-layer encryption in DWDM transponders protects whole wavelengths between sites.
Worked problem
MACsec overhead
With 1500-byte packets, each frame occupies 1538 bytes of wire time (Lesson 1). MACsec adds 32 bytes. By what percentage does the useful throughput fall? What if the network uses 9000-byte jumbo frames?
Show solution
- Standard frames: efficiency falls from \(1500/1538 = 97.5\%\) to \(1500/1570 = 95.5\%\), a relative loss of \(1 - 1538/1570 = 2.0\%\).
- Jumbo frames: from \(9000/9038\) to \(9000/9070\), a relative loss of \(1 - 9038/9070 = 0.35\%\).
Answer: About 2% with standard frames and about 0.35% with jumbo frames. The hardware adds negligible latency, so MACsec is a cheap way to protect links between buildings. The larger concern is key management and making sure the encryption does not fail closed during an outage.
A longer-term concern is that large quantum computers, if built, could break the public-key algorithms used to exchange encryption keys. Data captured today could be decrypted later ("harvest now, decrypt later"), so operators are beginning to adopt the post-quantum key exchange algorithms standardized by NIST in 2024 for long-lived sensitive traffic.
Network services that applications depend on
Several small services are critical: if they fail, everything fails.
- DNS (Domain Name System) translates names into addresses. Data centres run their own resolvers and authoritative servers, replicated widely; a DNS failure makes healthy services unreachable.
- DHCP assigns addresses to servers as they boot, and network booting (PXE) lets new servers install their operating systems automatically.
- NTP and PTP keep clocks synchronized (Lesson 10). Logs, certificates, databases and distributed systems all depend on accurate time.
- Authentication services (such as RADIUS or TACACS+ for network devices) control who can log in to switches and routers.
Each of these needs redundancy across failure domains and must remain available during an outage of the main network, a lesson several major outages have taught (Lesson 12).
Common mistakes
MistakeRelying on a perimeter firewall alone.
InsteadSegment the network, apply least privilege east-west and assume an intruder may already be inside.
MistakeConnecting building management systems to the corporate network for convenience.
InsteadIsolate OT networks and tightly control any remote access.
MistakeUsing modulo hashing for server pools that change size.
InsteadUse consistent hashing to limit disruption.
MistakeExpecting the data centre's own links to absorb a large DDoS attack.
InsteadArrange upstream scrubbing or CDN protection in advance.
MistakeRunning management access over the production network only.
InsteadProvide an independent out-of-band network to recover from failures.
Summary and key terms
- VLANs, VRFs and overlays isolate tenants on a shared fabric; clouds build VPCs in host software.
- SR-IOV, SmartNICs and DPUs move virtual switching, security and encryption into hardware.
- Load balancers spread traffic at layer 4 or 7 with health checks; anycast and consistent hashing scale them.
- Security rests on defence in depth, least privilege, segmentation and zero trust.
- Management and building OT networks must be isolated and independently reachable.
- DDoS attacks can exceed any site's capacity and must be absorbed upstream.
- MACsec, IPsec, TLS and optical encryption protect traffic, with modest overhead.
- DNS, DHCP, time and authentication services are small but critical dependencies.
- Tenant
- A customer or application needing an isolated network.
- VRF
- A separate routing table for one tenant on shared equipment.
- VPC
- A virtual private cloud: a tenant's isolated network in a public cloud.
- DPU
- A data processing unit: a network card with processors that offload networking and security.
- Load balancer
- A device or service that spreads connections across servers.
- Consistent hashing
- A hashing method that moves few keys when servers are added or removed.
- Microsegmentation
- Security policy applied to each workload individually.
- Zero trust
- Authenticating and authorizing every connection regardless of network location.
- DDoS
- A distributed denial-of-service attack from many sources.
- MACsec
- Link-layer encryption for Ethernet (IEEE 802.1AE).
Practice problems
Work each problem on paper first, then reveal the answer to check.
How many segments can a 24-bit VXLAN identifier distinguish?
Show answer
2²⁴ = 16,777,216.
What lets two tenants use the same private addresses on one router?
Show answer
Separate VRFs.
Why do cloud providers use DPUs?
Show answer
To offload networking, security and storage from host CPUs and isolate them from the host.
Layer 4 vs layer 7 load balancing?
Show answer
Layer 4 uses addresses and ports; layer 7 reads application data such as HTTP.
With modulo hashing, roughly what fraction of keys move when going from 20 to 21 servers?
Show answer
About 20/21, or 95%.
What does least privilege mean for a web server?
Show answer
It can reach only the systems and ports it needs.
Two 100 Gb/s links carry 50 Gb/s of normal traffic when a 450 Gb/s attack arrives. Fraction delivered if drops are even?
Show answer
200/500 = 40%.
MACsec adds 32 bytes to a 1538-byte frame slot. Relative throughput loss?
Show answer
About 2%.
Why must the out-of-band network be independent?
Show answer
So engineers can reach equipment when the production network fails.
Name four critical network services.
Show answer
DNS, DHCP, time (NTP/PTP), authentication.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.