
CSCO-121 · Lesson 3 of 12 · 23 min
Threats, vulnerabilities and risk
▶ Video coming soon A video version of this lesson is on the way.
On Jordan's second shadowing afternoon, Keisha handed him a sticky note with three words: asset, threat, vulnerability. "Clients ask me if they are secure," she said. "That question has no answer. What I can answer is: what do you have that is worth protecting, who or what might harm it, and where are you weak? Put those together and you have risk, and risk is something we can actually manage." She asked him to come back in an hour with those three lists for Prairie Paws Veterinary Clinic.
This lesson defines the vocabulary that the rest of the course depends on. The exam expects you to tell a threat from a vulnerability, to recognize the kinds of people and events that threaten organizations, to understand how likelihood and impact combine into risk, and to know the four basic ways an organization can respond to a risk. CSCO-122 builds on this with vulnerability scanning and formal risk frameworks.
Assets
An asset is anything of value to the organization that could be harmed. Assets include data, such as patient records, client files and payment information; systems, such as servers, laptops, point-of-sale terminals and cloud accounts; people and their knowledge; physical things such as buildings and equipment; and less tangible things such as reputation and the trust of customers. Security starts with knowing what you have. You cannot protect a server you do not know exists, and you cannot judge the harm of losing a database if you do not know what is in it.
Jordan's asset list for Prairie Paws was longer than he expected: the practice-management application and its database of animal and owner records, 18 PCs across two locations, a reception kiosk, label printers, the clinic's email accounts, the payment terminal, the backup drive, the website and booking form, the Wi-Fi networks, and the veterinarians' own knowledge of their systems. Keisha added two he had missed: the clinic's online reviews, which a breach could damage, and the controlled-drug log, which regulators expect to be accurate.
Threats and threat actors
A threat is anything that could exploit a weakness and cause harm to an asset. Some threats are deliberate, some accidental and some natural. A threat actor is the person or group behind a deliberate threat. Thinking about who might attack, and why, helps defenders decide which threats are realistic for a given organization. A small veterinary clinic is unlikely to be targeted by a foreign intelligence service, but it is very likely to receive phishing emails from criminals who send millions of them.
| Threat actor | Typical motive | Typical capability | Example concern for a small client |
|---|---|---|---|
| Cybercriminals | Money | Low to high; many use ready-made tools and services | Ransomware, invoice fraud, stolen payment data |
| Hacktivists | Ideology or publicity | Low to moderate | Defaced website, leaked data to embarrass |
| Nation-state groups | Espionage, disruption | Very high and patient | Rare for small firms, but suppliers can be caught up |
| Insiders | Revenge, money, carelessness | Already have access | Former staff whose accounts were never removed |
| Opportunists | Curiosity, bragging | Low; rely on easy targets | Default passwords, exposed devices |
| Competitors | Advantage | Varies | Theft of client lists or pricing |
Not every threat is a person. Hardware failure, power outages, fire, flood and severe weather are environmental threats. Human error is one of the most common threats of all: an employee who emails a file to the wrong address, deletes the wrong folder, or leaves a laptop on a bus. A good threat list includes all of these. Keisha told Jordan that, in her experience, more small-business incidents start with a mistake or an unpatched system than with a clever attacker.
Vulnerabilities
A vulnerability is a weakness that a threat could exploit. Vulnerabilities can be technical, such as software with a known flaw, a default password on a printer, a firewall rule that allows too much, or an unencrypted wireless network. They can be procedural, such as no process for removing accounts when staff leave or no verification when someone asks to change payment details. They can be physical, such as an unlocked server cupboard, and human, such as staff who have never been shown what phishing looks like.
Publicly known software vulnerabilities are given identifiers in the Common Vulnerabilities and Exposures system, so a flaw might be called CVE-2026 followed by a number. The Common Vulnerability Scoring System, CVSS, gives each one a severity score from 0 to 10. These shared names and scores let vendors, defenders and tools talk about the same flaw. A zero-day vulnerability is one that attackers know about before the vendor has released a fix, so defenders have had zero days to patch. CSCO-122 covers how to find vulnerabilities and read scan results.
An exploit is the method or code that takes advantage of a vulnerability. When a threat actor uses an exploit against a vulnerability in an asset, the result is a security incident. Defenders do not need to know how to write exploits; they need to know that vulnerabilities exist, how to find and fix them, and how to tell when one is being used.
Risk
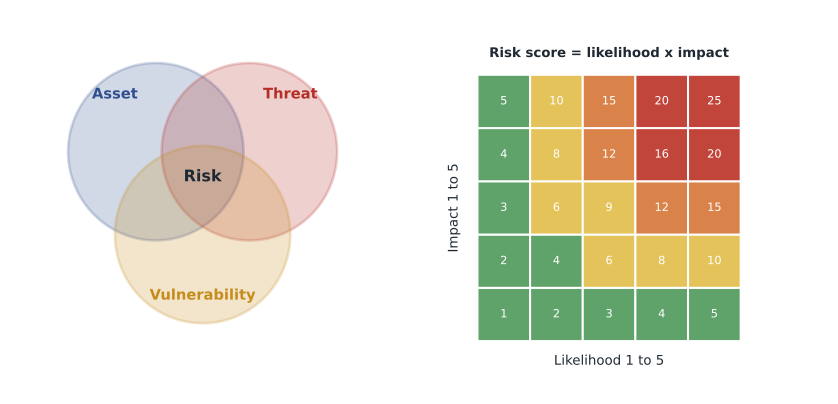
Risk is the possibility of harm when a threat exploits a vulnerability in an asset. It is usually described by two factors: likelihood, how probable the event is, and impact, how bad the harm would be if it happened. A risk that is both likely and harmful needs attention first. A risk that is unlikely and minor may not be worth spending money on. If any of the three parts is missing, there is little risk: a vulnerable server that holds nothing of value and is not reachable by any threat is a low priority.
Many organizations rank risks on a simple grid. Each risk is given a likelihood score and an impact score, for example from 1 to 5, and the two are multiplied to give a risk score from 1 to 25. This is called qualitative or semi-quantitative analysis. It is quick and good for comparing risks, though the scores are judgments rather than measurements. Quantitative analysis puts money on the table instead, using measures such as the expected loss from one event and how often the event is expected to happen in a year.
Inherent risk, residual risk and the risk register
Risk analysts distinguish inherent risk, the risk before any controls are applied, from residual risk, the risk that remains afterward. Comparing the two shows how much a control is worth. Phishing at Prairie Paws might score 16 before controls; with mail filtering, training and multi-factor sign-in it might fall to 6. The difference is the value of those controls, and the remaining 6 is what the clinic must decide to accept or reduce further.
Most organizations keep a risk register, a simple table that lists each risk with its description, owner, likelihood, impact, score, chosen response, planned controls and review date. For Brightline's small clients, the register is often a single spreadsheet that Keisha reviews with the owner twice a year. It is not glamorous, but it turns security from a collection of worries into a list of decisions, each with a name beside it.
Worked problem
Ranking three risks
Jordan scores three risks at Prairie Paws on a 1 to 5 scale. Phishing leading to a stolen email account: likelihood 4, impact 3. A failed backup drive discovered during a restore: likelihood 2, impact 5. Theft of the label printer: likelihood 2, impact 1. Rank them.
Show solution
- Risk score = likelihood × impact.
- Phishing: 4 × 3 = 12.
- Failed backup: 2 × 5 = 10.
- Printer theft: 2 × 1 = 2.
Answer: Phishing ranks first (12), the backup second (10) and the printer last (2). The clinic should address phishing and backup testing before worrying about the printer.
Worked problem
Expected yearly loss
The bakery estimates that one Saturday outage of its point-of-sale system costs about 2,500 dollars in lost sales and staff time. Based on past years, it expects such an outage about 0.4 times a year. What is the expected yearly loss, and is a 600-dollar-a-year backup internet connection worth it if it would prevent most of those outages?
Show solution
- The single loss expectancy (SLE) is 2,500 dollars.
- The annual rate of occurrence (ARO) is 0.4.
- Annual loss expectancy (ALE) = SLE × ARO = 2,500 × 0.4 = 1,000 dollars a year.
- The control costs 600 dollars a year, less than the 1,000 dollars of expected loss it would mostly prevent.
Answer: The expected loss is about 1,000 dollars a year, so a 600-dollar control that prevents most outages is good value.
risks = {"Phishing, stolen mailbox": (4, 3), "Backup fails on restore": (2, 5),
         "Guest Wi-Fi reaches staff PCs": (3, 4), "Label printer stolen": (2, 1)}
for name, (l, i) in sorted(risks.items(), key=lambda kv: -kv[1][0] * kv[1][1]):
    s = l * i
    band = "high" if s >= 12 else "medium" if s >= 6 else "low"
print(f"{s:>2} {band:<6} {name}")12 high Phishing, stolen mailbox 12 high Guest Wi-Fi reaches staff PCs 10 medium Backup fails on restore 2 low Label printer stolen
Responding to risk
Once a risk is understood, the organization decides what to do about it. There are four classic responses. Mitigation, also called reduction, means applying controls that lower the likelihood or the impact: training staff, adding multi-factor sign-in, patching software, separating networks. Transfer means shifting some of the financial impact to someone else, usually through cyber insurance or a contract with a supplier. Avoidance means stopping the activity that creates the risk, such as no longer storing card numbers at all. Acceptance means deciding to live with the risk, usually because it is small or because the cost of controls is higher than the expected harm.
Acceptance must be a deliberate decision by someone with the authority to make it, and it should be written down. Ignoring a risk is not the same as accepting it. Transfer does not remove the risk either: insurance may pay for recovery, but the clinic still has to tell its clients about a breach and live with the damage to its reputation. After controls are applied, some risk always remains; this is residual risk. The goal is to bring residual risk down to a level the organization is willing to accept, which is often called its risk appetite.
| Response | What it means | Prairie Paws example |
|---|---|---|
| Mitigate | Apply controls to reduce likelihood or impact | Phishing training and multi-factor sign-in for email |
| Transfer | Shift financial impact to another party | A cyber insurance policy |
| Avoid | Stop the activity that creates the risk | Stop keeping scanned copies of owners' ID cards |
| Accept | Knowingly live with the risk | Accept the small risk of label printer theft |
Threat intelligence
Threat intelligence is information about current threats that helps defenders make decisions: which vulnerabilities attackers are using now, which phishing themes are circulating, and which kinds of businesses are being targeted. Sources include national agencies, vendors' security blogs, industry sharing groups and the alerts built into security tools. For a small managed-services provider like Brightline, the most useful intelligence is often simple: an agency alert saying that a widely used remote-access product has a flaw being exploited, which tells Keisha to check every client that uses it today.
Keisha keeps a short list of sources and reads them daily. She also records what Brightline sees across its 40 clients, because a phishing campaign that hits one client this morning often hits three more by the afternoon. That local intelligence is shared in the team chat and used to update mail filters. CSCO-122 returns to threat intelligence as part of vulnerability management.
Common mistakes
MistakeCalling an unpatched server a threat.
InsteadThe unpatched server has a vulnerability; the threat is whoever or whatever might exploit it.
MistakeTreating risk as only likelihood or only impact.
InsteadRisk combines both.
MistakeIgnoring a risk and calling it accepted.
InsteadAcceptance is a recorded decision by someone with authority.
MistakeAssuming insurance removes the risk.
InsteadTransfer moves some financial impact; the incident and reputational harm remain.
MistakeListing only attackers as threats.
InsteadHuman error, hardware failure and natural events are threats too.
Summary and key terms
- An asset is anything of value; a threat is anything that could cause harm; a vulnerability is a weakness a threat could exploit.
- Threat actors include cybercriminals, hacktivists, nation-state groups, insiders and opportunists, each with typical motives.
- CVE identifiers name known vulnerabilities and CVSS scores their severity; a zero-day has no fix yet.
- Risk combines likelihood and impact; qualitative grids and quantitative measures such as ALE = SLE × ARO help rank it.
- The four risk responses are mitigate, transfer, avoid and accept; residual risk remains after controls.
- Threat intelligence tells defenders what attackers are doing now.
- Asset
- Anything of value to an organization that could be harmed.
- Threat
- Anything that could exploit a vulnerability and cause harm.
- Threat actor
- A person or group behind a deliberate threat.
- Vulnerability
- A weakness that a threat could exploit.
- Exploit
- A method or code that takes advantage of a vulnerability.
- Zero-day
- A vulnerability known to attackers before a fix is available.
- Risk
- The possibility of harm, judged by likelihood and impact.
- Residual risk
- The risk that remains after controls are applied.
- ALE
- Annual loss expectancy, single loss expectancy times annual rate of occurrence.
Practice problems
Work each problem on paper first, then reveal the answer to check.
A printer still uses its factory default password. Is that a threat or a vulnerability?
Show answer
A vulnerability.
What two factors are combined to rank a risk?
Show answer
Likelihood and impact.
An event costs 4,000 dollars and is expected 0.25 times a year. What is the ALE?
Show answer
1,000 dollars a year.
Name the four risk responses.
Show answer
Mitigate, transfer, avoid and accept.
What is a zero-day vulnerability?
Show answer
A flaw attackers know about before the vendor has released a fix.
Why is human error included in threat lists?
Show answer
Mistakes cause many real incidents, even without an attacker.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.