
ACCT-240 · Lesson 11 of 12 · 25 min
Cybersecurity, fraud prevention and privacy for accountants
Accounting systems hold exactly what criminals want: money movement instructions, bank details, payroll records, tax numbers and confidential financial results. Accountants are not expected to be security engineers, and this lesson stays at the level of governance and everyday practice. But accountants are often the last line of defence against payment fraud, they own much of the sensitive data, and they are responsible for the controls that would detect a loss. The CISSP courses and CMPUT-331 cover security technology in depth; here we focus on what a finance team needs to know and do.
The guiding idea is that most losses in finance functions come not from technical break-ins but from someone being persuaded to do something they should not: change a supplier's bank account, pay an urgent invoice, send a payroll file, approve a transfer. Good controls make those actions require verification by a second channel and a second person, so that a single convincing email cannot move money.
Governance of information security
Information security protects confidentiality (only authorized people see data), integrity (data is accurate and not altered without authorization) and availability (systems and data are there when needed). Responsibility starts with the board and senior management, who set the risk appetite, approve policies and fund the program. Most organizations base their program on a recognized framework such as the NIST Cybersecurity Framework 2.0 (2024), with its functions govern, identify, protect, detect, respond and recover, or the ISO/IEC 27001 standard for information security management systems. Finance leaders should know which framework their organization uses, who the security lead is, how incidents are reported and which finance systems and data are classified as most sensitive.
| Area | What finance should expect to see | Why it matters to accountants |
|---|---|---|
| Identity and access | Unique accounts, multifactor authentication (MFA), least privilege, prompt removal of leavers | Stolen passwords are the most common way into finance systems |
| Backups and recovery | Regular, tested backups kept offline or immutable; a recovery plan for the ERP and bank access | Ransomware can stop invoicing, payroll and the close |
| Patching and endpoint protection | Systems updated promptly; managed laptops with encryption | Unpatched or lost devices expose data |
| Awareness training | Regular training and practice on suspicious requests | People approve payments; they must recognize pressure tactics |
| Incident response | A documented plan with roles, including finance and legal | Fast action can recall payments and limit reporting obligations |
| Third-party risk | Review of vendors that hold or process company data | A supplier's breach can expose the company's data or payments |
Payment fraud and business email compromise
Business email compromise (BEC) is a fraud in which criminals use a hijacked or look-alike email account to persuade staff to send money or sensitive data. Common versions include a supplier "changing banks" just before a large payment, an executive asking for an urgent confidential transfer, and an employee asking payroll to update their direct deposit account. The FBI's Internet Crime Complaint Center has reported BEC as one of the costliest categories of cybercrime for years, with reported losses of roughly US$2.8 billion in 2024 alone, and Canadian authorities report similar patterns. BEC succeeds because the message looks routine and creates time pressure, not because of technical sophistication. The defence is procedural.
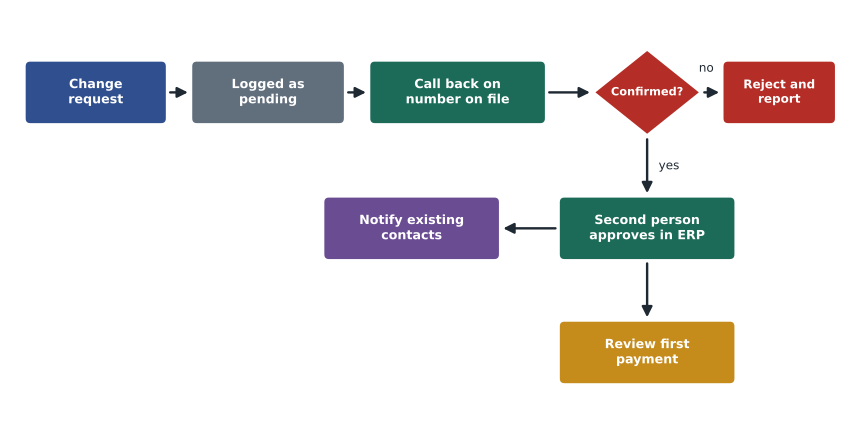
The central control is out-of-band verification. Any request to change payment instructions, whether for a supplier, an employee or a customer refund, is confirmed by calling the counterparty on a phone number already on file or obtained independently, never the number in the request. The person who verifies should be different from the person who received the request, the call should be documented, and the change should not take effect until the verification is complete. Many organizations add a cooling-off period, so that the first payment after a bank change is held or limited, and they send a confirmation notice to the old contact details, which alerts a genuine supplier if a fraudster made the change.
# Ridgeback: rules that hold risky payment-instruction changes for verification (illustrative)
requests = [
    {"id": "CR-301", "party": "Northwind Textiles", "type": "supplier bank", "channel": "email",
     "days_before_payment": 2, "amount_due": 48200, "callback_done": False},
    {"id": "CR-302", "party": "Alpine Buckle Co", "type": "supplier address", "channel": "portal",
     "days_before_payment": 20, "amount_due": 4300, "callback_done": False},
    {"id": "CR-303", "party": "B. Okafor", "type": "employee deposit", "channel": "email",
     "days_before_payment": 1, "amount_due": 2418, "callback_done": True},
]
for r in requests:
    holds = []
    if r["type"] in ("supplier bank", "employee deposit") and not r["callback_done"]:
        holds.append("call back on number already on file")
    if r["channel"] == "email" and r["type"] != "supplier address":
        holds.append("second approver required for email-initiated change")
    if r["days_before_payment"] <= 3 and r["amount_due"] > 10000:
        holds.append("hold next payment for review")
    status = "HOLD: " + "; ".join(holds) if holds else "proceed with normal approval"
print(f"{r['id']} {r['party']:20s} {r['type']:17s} -> {status}")CR-301 Northwind Textiles supplier bank -> HOLD: call back on number already on file; second approver required for email-initiated change; hold next payment for review CR-302 Alpine Buckle Co supplier address -> proceed with normal approval CR-303 B. Okafor employee deposit -> HOLD: second approver required for email-initiated change
The rules hold the email request to change Northwind's bank account two days before a $48,200 payment on three grounds, which is exactly the pattern of a typical BEC attempt. The employee deposit change has been verified by phone but still needs a second approver because it came by email. The address change through the supplier portal follows the normal approval route. Rules like these can be built into the ERP's workflow, so that the system, not an individual's memory under pressure, enforces the procedure.
Building a security-aware finance culture
Controls work only when people follow them under pressure, and attackers deliberately create pressure: a request arrives late on a Friday, claims to come from the chief executive, and insists on secrecy. A finance culture that supports controls makes it normal, and even praised, to slow down and verify. Leaders reinforce this by following the procedures themselves and by never asking staff to bypass them for convenience. Practical steps include short, regular training using real examples of attempted fraud, simulated phishing exercises used for learning rather than blame, a simple way to report a suspicious message, and clear authority for any staff member to hold a payment until it is verified. Finance managers should also review the policy exceptions and overrides recorded in the ERP, because a pattern of urgent exceptions is itself a warning sign that procedures are being worn down.
Other fraud prevention controls in finance
Payment fraud is one part of a wider fraud risk program. BUS-310 discussed the fraud triangle of pressure, opportunity and rationalization, and the role of ethics and whistleblowing. In the AIS, the most effective controls reduce opportunity: segregation of duties (lesson 8), restricted access to bank portals with dual authorization for transfers, positive pay (lesson 6), daily bank reconciliations, monitoring of changes to master data, mandatory vacations, and data analytics run regularly over payments, payroll, credit memos and journal entries. Detection matters too. Surveys by the Association of Certified Fraud Examiners consistently find that tips are the most common way occupational fraud is detected, which is why an accessible, trusted reporting channel is part of internal control.
Privacy and records retention
Accounting systems hold large amounts of personal information about employees, customers and suppliers who are individuals. In Canada, the Personal Information Protection and Electronic Documents Act (PIPEDA) governs private-sector organizations in most provinces. It requires consent for collection and use, limits use to identified purposes, requires safeguards appropriate to the sensitivity of the data, and, since November 2018, requires organizations to report breaches of security safeguards that create a real risk of significant harm to the Privacy Commissioner and affected individuals, and to keep records of all breaches for 24 months. Alberta, British Columbia and Quebec have their own private-sector laws. Quebec's Law 25, phased in between 2022 and 2024, adds requirements such as a designated person responsible for personal information, privacy impact assessments for new systems, a register of confidentiality incidents and stricter consent rules. Federal legislation to replace PIPEDA has been proposed but, as of October 2026, PIPEDA remains in force; check its current status.
Privacy principles translate into specific AIS practices. Collect only the personal data needed (data minimization). Restrict access to payroll, banking and identification fields to those who need them, and mask them in reports. Encrypt sensitive data in storage and transmission. Keep a record of which systems hold personal data and which vendors process it. Build privacy review into system changes and new tools, including AI tools that might send data outside the organization. And delete data when it is no longer needed, which brings in records retention rules.
Records retention rules set the minimum time that accounting records must be kept, and privacy law encourages organizations not to keep personal data longer than needed. The Canada Revenue Agency generally requires books and records, including supporting documents, to be kept for six years from the end of the last tax year to which they relate, and longer in some cases, such as when an objection or appeal is under way or for certain permanent records. Records may be kept electronically if they are readable and accessible. Provincial laws, corporate statutes and contracts can require longer periods, so organizations should set a retention schedule covering each type of record.
Worked problem
Responding to a suspected BEC payment
On Thursday morning Ridgeback's AP clerk notices that a $48,200 payment sent to Northwind Textiles on Tuesday went to a new bank account changed by email the day before, and Northwind says it never sent the request. What should Ridgeback do, in order?
Show solution
- Immediately contact Ridgeback's bank to request a recall of the funds; speed matters because funds are often moved within hours or days.
- Notify the incident response lead and preserve evidence: the emails with full headers, the change log and the payment records.
- Report the fraud to law enforcement (in Canada, the local police and the Canadian Anti-Fraud Centre; in the US, the FBI's IC3), which can help with recovery.
- Reverse the bank detail change, review other recent master data changes and check whether the email account was compromised.
- Afterwards, assess whether the verification control failed or was bypassed, fix the gap, and determine the accounting treatment: the loss is recorded when recovery is not expected, and the supplier is still owed.
Answer: Recall the funds first, then preserve evidence, report, contain and fix the control; Northwind is still owed the $48,200.
Common mistakes
MistakeVerifying a bank change by calling the number in the request.
InsteadCall a number already on file or obtained independently.
MistakeLetting the person who received a change request also approve it.
InsteadRequire a second, independent approver for payment instruction changes.
MistakeTreating security as purely an IT responsibility.
InsteadFinance owns payment controls, sensitive data and incident response steps.
MistakeKeeping personal data forever just in case.
InsteadFollow a retention schedule and delete data no longer needed.
MistakeWaiting to report a fraudulent payment until the facts are complete.
InsteadContact the bank immediately; recall chances fall quickly.
Summary and key terms
- Most finance losses come from persuading staff to act, not from technical break-ins.
- Security protects confidentiality, integrity and availability, under board-level governance and a recognized framework.
- Business email compromise is countered by out-of-band verification, separate approval and payment holds.
- Fraud controls reduce opportunity and improve detection, including trusted reporting channels.
- PIPEDA, provincial laws and Quebec's Law 25 govern personal information and breach reporting.
- Privacy practices include minimization, restricted access, masking, encryption and deletion.
- The CRA generally requires records to be kept six years from the end of the related tax year.
- Confidentiality, integrity and availability
- The three core objectives of information security.
- Multifactor authentication
- Logging in with two or more independent factors, such as a password and a phone prompt.
- Business email compromise
- Fraud using hijacked or look-alike email to obtain payments or data.
- Out-of-band verification
- Confirming a request through a separate, trusted channel.
- Ransomware
- Malicious software that blocks access to data until a ransom is paid.
- Incident response plan
- A documented plan for detecting, containing and recovering from security incidents.
- Data minimization
- Collecting and keeping only the personal data needed for a purpose.
- Masking
- Hiding all or part of a sensitive field, such as showing only the last four digits.
- Retention schedule
- A list of how long each type of record must be kept.
- Third-party risk
- Risk arising from vendors and partners that access or hold an organization's data.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Why is BEC described as a procedural rather than technical problem?
Show answer
It works by persuading staff to act; the defence is verification procedures and separate approvals.
Describe out-of-band verification for a supplier bank change.
Show answer
Call the supplier on a number already on file, document the call, and have a second person approve the change.
In the code example, why was CR-301 held?
Show answer
Bank change by email, no callback, and a payment over $10,000 due within three days.
Why send a confirmation notice to the supplier's old contact details?
Show answer
A genuine supplier will notice and object if a fraudster made the change.
Name the six functions of the NIST Cybersecurity Framework 2.0.
Show answer
Govern, identify, protect, detect, respond and recover.
What is the most common way occupational fraud is detected, according to ACFE surveys?
Show answer
Tips from employees, customers or suppliers.
When must a PIPEDA breach be reported?
Show answer
When a breach of security safeguards creates a real risk of significant harm.
Give three privacy practices for an AIS.
Show answer
Data minimization, restricted access with masking, encryption (also deletion under a retention schedule).
How long does the CRA generally require records to be kept?
Show answer
Six years from the end of the last tax year to which they relate.
What is the first step after discovering a fraudulent payment?
Show answer
Contact the bank immediately to request a recall.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.