
MSAZ-342 · Lesson 11 of 12 · 19 min
Post-incident review
▶ Video coming soon A video version of this lesson is on the way.
An incident is not finished when the account is back in use. The last stage of the response lifecycle is learning from it: what happened, what went well, what did not, and what will change. Harrow & Finch holds a post-incident review for every high-severity incident within ten working days. The review for incident 4196 is planned for Friday, November 20, 2026, with Nadia leading and Ama, Sunil, Carmen Ortiz and the merchandising manager attending. This lesson follows how Ama prepared it between November 13 and 15: building the timeline, measuring the response, deciding the breach question for each country, and turning findings into owned, dated actions.
A blameless review
The purpose of a review is to improve the system, not to find someone to blame. People in a review speak openly only if they are confident that what they say will not be used against them, and a review that hides mistakes cannot fix the conditions that produced them. Nadia opened every review with the same statement: we assume everyone acted reasonably with the information they had at the time, and we are here to change what they had. Theo clicked a convincing link to a fake shared document; the question is not why he clicked, but why a click could lead to a compromised account, and why it took 17 hours to notice.
| Review question | For 4196 |
|---|---|
| What happened, in order? | The timeline below, built from logs and incident comments |
| What went well? | The analytics rule fired five minutes after the first malicious sign-in; containment took 42 minutes from the alert |
| What did not go well? | No detection of the phishing click or the session theft until the attacker changed MFA; the file downloads had no alert |
| Why? | No rule for session reuse from a second country; no rule for downloads from new countries; contractors used passwords and app MFA |
| What will we change? | The actions table, each with an owner and a date |
Building the timeline
The timeline is the backbone of the review. It should be built from evidence, not from memory, and every entry should say where it came from. Ama started from the incident comments, added the events from the logs that no alert had covered, and checked each time against its source. Times are shown in local time with UTC noted once at the top, because the review's readers think in local time.
| Time (local, Nov 11 to 13) | Event | Source |
|---|---|---|
| Nov 11 16:18 | Phishing message delivered to three addresses | EmailEvents |
| Nov 11 16:20 | Theo opens the link and signs in through the kit page | UrlClickEvents, SigninLogs |
| Nov 12 07:45 | Theo signs in normally from home | SigninLogs |
| Nov 12 09:57 | Sign-in from abroad reusing the session | SigninLogs |
| Nov 12 09:58 | New authenticator app registered | AuditLogs |
| Nov 12 10:02 | Analytics rule fires; incident 4196 created | SecurityIncident |
| Nov 12 10:06 | Inbox rule created | OfficeActivity |
| Nov 12 10:09 | Ama acknowledges | Incident activity log |
| Nov 12 10:15 | Two files downloaded from the merchandising site | OfficeActivity |
| Nov 12 10:44 | Account disabled, sessions revoked | AuditLogs, incident comments |
| Nov 13 11:15 | Account re-enabled with a passkey | AuditLogs |
| Nov 13 16:40 | Incident resolved, true positive | SecurityIncident |
Two points on the timeline were new to the team. The UrlClickEvents table showed that Safe Links had checked the URL at click time and allowed it, because the page was not yet known to be malicious; the kit had moved to a new domain that morning. And the session that the attacker reused had been created at 16:20 on November 11 when Theo signed in through the kit page; his normal sign-in at 07:45 the next morning was a separate session. The attacker waited 17 and a half hours before using the stolen one, perhaps to avoid looking unusual during a working afternoon.
Measuring the response
Response metrics turn the timeline into numbers that can be compared across incidents. The definitions vary between organizations, so the review states them. Harrow & Finch uses four. Time to detect runs from the first malicious activity to the first alert. Time to acknowledge runs from the alert to an analyst taking ownership. Time to contain runs from the alert to the attacker losing access. Time to resolve runs from the alert to the incident being closed. Averages are often called MTTD, MTTA, MTTC and MTTR, the M standing for mean, but with small numbers of incidents the median is more honest, because one long incident pulls the mean a long way.
SecurityIncident
| where CreatedTime between (datetime(2026-11-01) .. datetime(2026-11-14))
| summarize arg_max(TimeGenerated, *) by IncidentNumber
| where Severity in ("High", "Medium") and Status == "Closed"
| extend Detect  = datetime_diff("minute", CreatedTime, FirstActivityTime),
         Ack     = datetime_diff("minute", FirstModifiedTime, CreatedTime),
         Resolve = datetime_diff("minute", ClosedTime, CreatedTime)
| summarize Incidents = count(),
            MedianDetect = percentile(Detect, 50),
            MedianAck = percentile(Ack, 50),
            MedianResolveHours = round(percentile(Resolve, 50) / 60.0, 1)
            by Severity
The query takes the latest record of each incident created in the first two weeks of November, keeps high and medium incidents that are closed, and computes three durations in minutes. FirstActivityTime is the earliest activity in the incident's alerts, which is the closest the table gets to the start of the attack; it is only as early as the first alert's evidence, which for 4196 was 09:57, not the click the day before. FirstModifiedTime is a usable stand-in for acknowledgment when the SOC's practice is to assign an incident as the first change. Time to contain is not a column; it comes from the comments, which is one more reason to write them carefully.
from statistics import median, mean
# minutes, high-severity incidents Nov 1-13 (Detect, Ack, Contain)
high = {
    4127: (14, 3, 2),     # attack disruption contained it automatically
    4155: (41, 12, 65),
    4191: (22, 8, 289),
    4196: (5, 7, 42),
}
for i, name in enumerate(("detect", "acknowledge", "contain")):
    vals = [v[i] for v in high.values()]
    print(f"time to {name:11}  median {median(vals):5.1f}  mean {mean(vals):5.1f}  max {max(vals)}")
# detection from the true start of 4196, the phishing click
click_to_alert = (24 * 60 + 10 * 60 + 2) - (16 * 60 + 20)
print(f"4196 from phishing click to alert: {click_to_alert} min = {click_to_alert/60:.1f} h")time to detect median 18.0 mean 20.5 max 41 time to acknowledge median 7.5 mean 7.5 max 12 time to contain median 53.5 mean 99.5 max 289 4196 from phishing click to alert: 1062 min = 17.7 h
What this code does
Four high-severity incidents from November each have three durations in minutes. The program prints the median, mean and maximum for each stage; for containment, the one long overnight incident makes the mean much larger than the median. It then measures 4196 from the phishing click at 16:20 on November 11 to the alert at 10:02 the next day: 1,062 minutes, or about 17.7 hours.
The numbers told two stories. Measured from the first malicious sign-in, 4196 was detected in five minutes. Measured from the click, it took almost 18 hours. Both are true, and the review recorded both, because the second is the one the actions should improve. The table also showed that the fastest containment of the month, incident 4127, was automatic: attack disruption acted before an analyst did. The review noted that as a reason to keep the signals that disruption depends on, such as Defender for Office 365 and Defender for Identity data, healthy and connected, since a gap there would quietly remove the fastest response the SOC has.
The breach decision
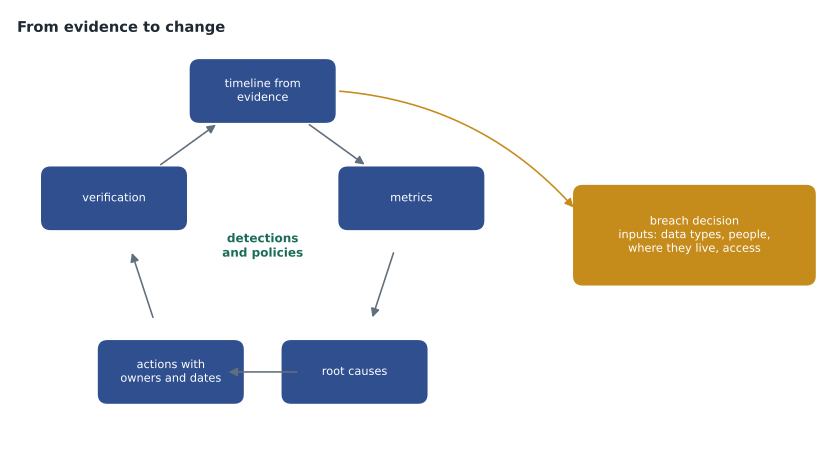
Every incident that touches personal information needs a recorded decision on notification. Carmen Ortiz made a preliminary assessment on November 13, which the review will confirm. The attacker read 64 messages in Theo's mailbox and downloaded two files: a planogram workbook and a store contact list with the names, work phone numbers and work email addresses of 23 store managers. The messages contained business correspondence with store managers and Brightfield staff, order quantities and layouts. One message included a Brightfield employee's personal mobile number. There was no customer information, no payment card data, no government identification numbers and no financial account details.
Iowa's breach notification law, Iowa Code chapter 715C, applies to breaches of security involving personal information of Iowa residents, which it defines as a name together with data such as a Social Security number, a driver's license or other government identification number, financial account details with a code that allows access, unique biometric data, or a unique electronic identifier or routing code with a code allowing access to a financial account. When a breach affects more than 500 Iowa residents, the attorney general must be notified within five business days of notifying consumers. None of the data in 4196 met that definition, so Carmen's assessment was that no notification was required. The company's incident response plan still requires the decision and its reasons to be documented, and outside counsel reviewed the assessment. Harrow & Finch told Brightfield about its employee's personal mobile number, because Brightfield's own obligations apply to its staff.
This course describes the law to explain how a SOC's evidence feeds the decision. The decision itself belongs to the privacy officer and legal advisers, and it depends on facts the SOC must supply accurately: what data, how many people, where they live, and whether the attacker could read it.
From findings to actions
A finding without an owner and a date is a hope. Ama drafted the actions table for Nadia to bring to the review, each tied to a gap on the timeline. Some were already done by November 15; the rest are plans.
| Gap | Action | Owner | Date |
|---|---|---|---|
| Session theft not detected until MFA change | Scheduled rule from the lesson 6 session query, hourly | Ama | Done Nov 13 |
| Downloads from a new country had no alert | Rule for file downloads from a country new for the user in 30 days | Ama | Nov 27 |
| Contractors used passwords and app MFA | Phishing-resistant authentication strength for all contractor accounts | Sunil | Dec 18 |
| Safe Links allowed a newly registered domain | Review Defender for Office 365 policies for newly registered domains | Sunil | Dec 4 |
| Copilot summaries missed unalerted events | Add session reuse and downloads to prompt guidance | Nadia | Nov 20 |
| 30-day evidence expiry | Export step added to the identity compromise task list | Ama | Done Nov 13 |
| Token theft generally | Evaluate token protection for supported apps | Sunil | Jan 2027 |
Each detection action ends with a test. For the session rule, Ama replayed the November 12 sign-ins through the query and confirmed it would have alerted at 10:00, two minutes before the existing rule. That is a small gain for this incident; the larger value is that a future attacker who does not change MFA would still be caught.
Sharing what was learned
The review produces two documents. The internal report, for the SOC and IT, has the full timeline, the evidence references and the actions. The summary for management is one page: what happened in plain words, the impact, the decision on notification and its reason, and the three actions that matter most. Carmen keeps the breach record. The coverage review from lesson 6 is updated, because Steal Web Session Cookie now has a tested rule, and the incident joins the training material: lesson 12 of this course is built from it.
Worked problem
Choosing the metric that matters
A manager reading the one-page summary asks: was this incident detected in five minutes or eighteen hours? How should the summary answer?
Show solution
- Give both numbers and what each starts from: five minutes from the attacker's first sign-in, about 18 hours from the phishing click.
- Explain that the five-minute figure shows the rule worked once the attacker acted, and the 18-hour figure shows where detection was missing.
- Point to the actions that address the gap: the session rule, phishing-resistant authentication for contractors and the Safe Links review.
- Avoid choosing the flattering number alone.
Answer: Both, each with its starting point, and tie the longer one to the actions that will shorten it.
Common mistakes
MistakeAsk who made the mistake.
InsteadAsk what conditions allowed the mistake to cause harm.
MistakeBuild the timeline from memory.
InsteadBuild it from logs and comments, with a source for each entry.
MistakeReport the mean of a handful of incidents.
InsteadReport medians, and state where each duration starts.
MistakeLeave the breach question unrecorded because nothing was reported.
InsteadRecord the decision and its reasons for every incident with personal information.
Summary and key terms
- Reviews are blameless: they change conditions, not people.
- The timeline comes from evidence, with a source for every entry.
- Define each metric's start and end; prefer medians for small numbers of incidents.
- The breach decision depends on what data, how many people, where they live and whether it was accessed; record it either way.
- Every finding becomes an action with an owner, a date and a test.
- Post-incident review
- A meeting and report that examine an incident to improve future response.
- Blameless review
- A review that assumes reasonable actions and focuses on conditions rather than individuals.
- Time to detect
- The time from first malicious activity to the first alert.
- Time to contain
- The time from the alert to the attacker losing access.
- Median
- The middle value of a sorted list, less affected by outliers than the mean.
- Breach record
- The documented assessment of a security incident involving personal information.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Why measure 4196 from the click as well as the sign-in?
Show answer
The click was the true start, and the 18-hour gap is what actions should shorten.
Why prefer medians here?
Show answer
With few incidents, one long incident distorts the mean.
What made the store contact list low risk?
Show answer
It held work contact details used for business communication.
What must every action have?
Show answer
An owner, a date and a test.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.