
ACCT-331 · Lesson 2 of 12 · 30 min
Professional ethics, independence and quality management
An audit is only worth what its independence is worth. If users believe the auditor is too close to management, too dependent on the client's fees, or too eager to sell other services, the opinion loses its value even if the work was technically sound. That is why every auditing framework begins with ethics. This lesson covers the fundamental principles that apply to all professional accountants, the conceptual framework for identifying and responding to threats, the specific independence rules for audit clients, and the firm-level systems of quality management that are meant to make good audits the norm rather than the exception. ACCT-211 and ACCT-212 dealt with professional judgment in applying accounting standards; here the question is whether the person exercising judgment can be trusted to do so objectively.
The fundamental principles
US CPAs are bound by the AICPA Code of Professional Conduct, state board rules and, for audits of issuers, the independence rules of the SEC and the PCAOB, which are stricter than the AICPA's in several areas. The AICPA Code is organized around principles that closely track the five fundamental principles of the international IESBA Code.
- Integrity: being straightforward and honest in all professional and business relationships.
- Objectivity: not allowing bias, conflict of interest or undue influence to override professional judgment.
- Professional competence and due care: maintaining the knowledge and skill needed for competent service and acting diligently under applicable standards.
- Confidentiality: respecting the confidentiality of information acquired through professional relationships and not using it for personal advantage.
- Professional behavior: complying with laws and regulations and avoiding conduct that discredits the profession.
Confidentiality has well-known exceptions. A professional accountant may, and sometimes must, disclose confidential information when required by law (for example, under a court order), when permitted by the client, or to respond to a practice inspection or disciplinary investigation. The IESBA Code's provisions on responding to non-compliance with laws and regulations (NOCLAR) go further: when an auditor becomes aware of an illegal act, the auditor must discuss it with management and those charged with governance, and in some cases consider disclosure to an appropriate authority even without client consent.
In the United States, Section 10A of the Securities Exchange Act of 1934 requires the auditor of an issuer that detects a likely illegal act to inform management and the audit committee and, if the board fails to take timely and appropriate remedial action on a material matter, to report to the SEC.
The conceptual framework: threats and safeguards
No rulebook can list every situation an auditor might face, so the codes use a conceptual framework. The accountant identifies threats to compliance with the fundamental principles, evaluates whether each threat is at an acceptable level, and addresses any threat that is not, by eliminating the circumstance, applying safeguards or declining the engagement. A reasonable and informed third party test applies: would a well-informed outsider, weighing all the facts, conclude that the accountant's objectivity is not compromised?
| Threat | What it means | Fairhaven illustration |
|---|---|---|
| Self-interest | A financial or other interest will inappropriately influence judgment | An audit senior owns Fairhaven shares through a self-directed account |
| Self-review | The auditor will evaluate work the firm itself performed | The firm designed the inventory costing module it now audits |
| Advocacy | The auditor promotes the client's position to the point that objectivity suffers | A partner speaks for Fairhaven in a tax dispute with the revenue agency |
| Familiarity | A long or close relationship makes the auditor too sympathetic | The engagement partner has led the audit for eight years and golfs with the CFO |
| Intimidation | The auditor is deterred from acting objectively by actual or perceived pressure | The CFO threatens to put the audit out to tender if the inventory write-down is proposed |
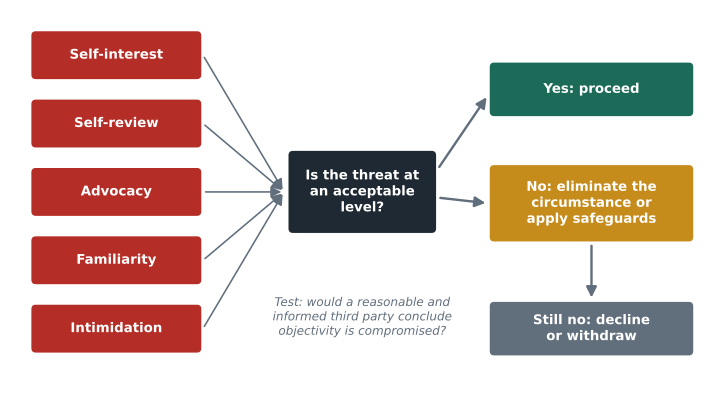
Safeguards are actions that reduce a threat to an acceptable level. Examples include assigning a partner who was not involved in a non-audit service to review that work, rotating senior staff, having an engagement quality reviewer examine significant judgments, and disclosing fees to the audit committee. Some threats are so significant that no safeguard is enough. Those are where the codes stop relying on judgment and impose outright prohibitions.
Independence of mind and in appearance
Independence has two parts. Independence of mind is the state of mind that lets the auditor form an opinion without being affected by influences that compromise judgment. Independence in appearance means avoiding facts and circumstances so significant that a reasonable and informed third party would conclude that the firm's integrity, objectivity or skepticism had been compromised. Both matter: an auditor who is privately objective but appears conflicted still undermines the value of the opinion.
Independence rules apply to the firm, to members of the engagement team and, for some interests, to close family members and other partners in the office. The main areas are financial interests, loans, business relationships, employment relationships, long association, fees and the provision of non-audit services.
- Financial interests: no member of the engagement team, and no partner in the office where the engagement partner practices, may hold a direct financial interest in an audit client, however small. Material indirect interests are also prohibited.
- Employment: a former engagement team member who joins the client in a key financial reporting role creates a threat; for listed clients there are cooling-off periods before senior audit staff can take such a role.
- Loans and business relationships: loans from the client are prohibited except ordinary loans on normal terms from a lending institution client; joint ventures with the client are prohibited.
- Fees: contingent fees for audits are prohibited, and fee dependence on a single client, overdue fees and fee pressure all create threats.
- Long association: SEC rules limit the lead and concurring partners on an issuer audit to five consecutive years, followed by five years off; other audit partners serve seven years with two off.
# Engagement partner rotation for a listed audit client (simplified rules)
def check(history, time_on, cooling):
    # history: years as engagement partner, in order; returns the first year the partner must step off
    run = 0
    for year in history:
        run += 1
        if run > time_on:
            return year
    return None
rules = {"Canada (IESBA-based codes)": (7, 5), "United States (SEC rules)": (5, 5)}
partner_years = list(range(2020, 2028))      # Dana Okafor has led the audit since 2020
for place, (on, off) in rules.items():
    stop = check(partner_years, on, off)
    msg = f"cannot lead the {stop} audit; may return for the {stop + off} audit" if stop else "no rotation needed yet"
print(f"{place:<28} {on} years on, {off} off: {msg}")Canada (IESBA-based codes) 7 years on, 5 off: cannot lead the 2027 audit; may return for the 2032 audit United States (SEC rules) 5 years on, 5 off: cannot lead the 2025 audit; may return for the 2030 audit
Non-audit services
Firms that audit public companies once earned more from consulting than from auditing, and the collapse of Enron in 2001, where Arthur Andersen earned large fees for both, led to strict limits. Today, for listed or public interest entity clients, the codes prohibit services that would create a self-review threat because the firm would audit its own work, or an advocacy or management-responsibility threat because the firm would act as management.
| Service | Issuer client (SEC and PCAOB rules) | |
|---|---|---|
| Bookkeeping and preparing financial statements | Prohibited | Prohibited |
| Designing or implementing financial information systems | Prohibited when it creates a self-review threat | Prohibited |
| Valuation services that affect the statements | Prohibited when material or subjective | Prohibited (appraisal and valuation) |
| Internal audit outsourcing | Prohibited when it relates to financial reporting controls | Prohibited |
| Acting as management or making management decisions | Prohibited | Prohibited |
| Legal services, expert services for advocacy | Generally prohibited | Prohibited |
| Tax compliance | Usually permitted with safeguards and audit committee approval | Permitted with audit committee pre-approval; aggressive tax shelters and contingent tax fees prohibited |
For public companies, the audit committee must pre-approve every service the auditor provides, audit and non-audit, and the company discloses the fees it paid in its annual proxy materials. These requirements make non-audit fees visible to shareholders. The program below summarizes Bramble Shaw's fees from Fairhaven for the year.
# Fee dependence and non-audit services at Bramble Shaw (illustrative, thousands of dollars)
firm_revenue = 48_000                       # the office's total annual fees
fees = {"audit": 385, "tax compliance": 60, "IT system advice": 240, "valuation for an acquisition": 180}
total = sum(fees.values())
non_audit = total - fees["audit"]
print(f"Total fees from Fairhaven: {total:,}")
print(f"Share of office revenue: {total / firm_revenue:.1%}")
print(f"Non-audit fees as a share of audit fee: {non_audit / fees['audit']:.0%}")
for service, fee in fees.items():
    flag = "review for threats" if service != "audit" else ""
    print(f"  {service:<30}{fee:>6}  {flag}")
limit = 0.15                                 # an illustrative fee-dependence threshold
print("Fee dependence above threshold" if total / firm_revenue > limit else "Fee dependence below threshold")Total fees from Fairhaven: 865 Share of office revenue: 1.8% Non-audit fees as a share of audit fee: 125% audit 385 tax compliance 60 review for threats IT system advice 240 review for threats valuation for an acquisition 180 review for threats Fee dependence below threshold
Two of the proposed services need attention. Advice on the design of the IT system that produces the financial statements would create a self-review threat and, for a listed client, is prohibited. A valuation used in the purchase price allocation for an acquisition is also likely prohibited because it would feed directly into the statements and is subjective. Tax compliance is normally permissible with audit committee approval. Fee dependence on Fairhaven is low, at under 2 percent of the office's revenue.
Professional skepticism
Independence makes objective judgment possible; professional skepticism is the habit of using it. Skepticism is an attitude that includes a questioning mind, alertness to conditions that may indicate misstatement due to error or fraud, and a critical assessment of evidence. It does not mean assuming management is dishonest. It means not accepting less than persuasive evidence because the auditor believes management is honest. Regulators repeatedly cite a lack of skepticism as a root cause of inspection findings, especially in the audit of accounting estimates, where management's assumptions are easy to accept and hard to challenge.
Skepticism is threatened by biases that everyone shares. Anchoring is the tendency to stick too closely to an initial figure, such as management's estimate. Confirmation bias is the tendency to look for evidence that supports a conclusion already reached. Automation bias is the tendency to trust output from a system or tool, including generative AI tools, without enough scrutiny. Good audit practice counters these by asking explicitly what evidence would contradict management's position and by seeking it.
Quality management at the firm
PCAOB QC 1000, A Firm's System of Quality Control, replaces the PCAOB's old interim quality control standards and takes effect on December 15, 2026, after the PCAOB postponed it by a year in August 2025. It requires a risk-based quality control system, an annual evaluation of that system and reporting to the PCAOB on a new form. For non-issuer audits, the AICPA's Statement on Quality Management Standards 1 and 2 (SQMS 1 and 2) took effect on December 15, 2025. AS 1220 deals with engagement quality reviews of issuer audits, and AS 1201 with supervision of the engagement team.
| Component | What the firm must address |
|---|---|
| Governance and leadership | A culture that values quality; leaders accountable for it |
| Relevant ethical requirements | Independence policies, monitoring of investments and services |
| Acceptance and continuance | Judging client integrity and the firm's ability to do the work |
| Engagement performance | Direction, supervision, review, consultation and differences of opinion |
| Resources | People, technology (including audit tools and AI), and intellectual resources |
| Information and communication | Getting relevant information to the right people |
| Risk assessment process | Setting quality objectives and identifying quality risks |
| Monitoring and remediation | Inspecting completed engagements, finding root causes and fixing them |
The engagement quality review is a key response for higher-risk audits, including all audits of listed entities. An experienced partner who is not part of the engagement team evaluates the significant judgments the team made and the conclusions it reached before the report is released. The reviewer does not redo the audit, but can refuse to concur, in which case the report cannot be issued until the matter is resolved.
The PCAOB expects QC 1000 to push firms toward the root cause analysis and monitoring that the international standards introduced in 2022; firms with more than 100 issuer clients must also have an external quality control function overseeing their systems (as of October 2026).
Audit committees and governance
The audit committee of the board is the auditor's main point of contact for governance matters. It recommends the appointment of the auditor, pre-approves services, oversees the auditor's work and receives the auditor's communications about significant findings. Its members must be independent directors and financially literate.
In the United States, Section 301 of Sarbanes-Oxley and SEC Rule 10A-3 set these requirements for listed issuers, and the exchanges add their own listing standards. AS 1301 sets out what the auditor must communicate to the audit committee, including significant risks, critical accounting estimates, uncorrected misstatements and difficult or contentious matters.
Worked problem
Evaluating a threat
Fairhaven's CFO asks Bramble Shaw to prepare the year-end journal entries for leases because her team is short-staffed. Can the firm do it?
Show solution
- Preparing journal entries is a bookkeeping service and a management responsibility.
- The firm would then audit entries it prepared itself, creating a self-review threat.
- Fairhaven is a listed entity, so the codes prohibit bookkeeping services outright.
Answer: No. The firm can explain the lease standard and comment on entries management prepares, but must not prepare them.
Worked problem
Fee pressure and intimidation
During the audit, Fairhaven's CFO says the board will tender the audit unless the proposed inventory write-down is dropped. What should the engagement partner do?
Show solution
- Recognize an intimidation threat to objectivity.
- Do not change the conclusion; evaluate the evidence for the write-down on its merits.
- Consult within the firm and communicate the matter to the audit committee, which appoints and oversees the auditor.
Answer: Stand by the evidence, consult and escalate to the audit committee; if the threat cannot be reduced, consider withdrawing.
Common mistakes
MistakeThinking a small shareholding in an audit client is acceptable if it is immaterial to the holder.
InsteadEngagement team members may not hold any direct financial interest in the client, however small.
MistakeTreating independence as a purely personal state of mind.
InsteadIndependence in appearance matters too; a reasonable third party must see no compromise.
MistakeAssuming non-audit services are fine if the audit committee approves them.
InsteadSome services are prohibited outright for public-company clients; pre-approval cannot cure them.
MistakeEquating skepticism with distrust of management.
InsteadSkepticism means demanding persuasive evidence and critically assessing it, not presuming dishonesty.
MistakeSeeing quality management as a checklist.
InsteadQC 1000 is risk-based: the firm sets objectives, identifies risks and designs responses.
Summary and key terms
- Five fundamental principles underlie the codes: integrity, objectivity, competence and due care, confidentiality and professional behavior.
- The conceptual framework identifies, evaluates and addresses self-interest, self-review, advocacy, familiarity and intimidation threats.
- Independence of mind and in appearance are both required.
- For issuer clients, lead and concurring partners rotate after five years under SEC rules.
- Many non-audit services are prohibited for public-company clients, and audit committees must pre-approve the rest.
- Professional skepticism counters anchoring, confirmation and automation bias.
- QC 1000 (from December 15, 2026) and SQMS 1 require risk-based quality systems.
- QC 1000
- The PCAOB standard on firms' quality control systems, effective December 15, 2026.
- Conceptual framework
- An approach that identifies, evaluates and addresses threats to the fundamental principles.
- Self-review threat
- The threat that an auditor will not properly evaluate work the firm itself performed.
- Familiarity threat
- The threat that a long or close relationship makes the auditor too sympathetic to the client.
- Intimidation threat
- The threat that pressure deters the auditor from acting objectively.
- Safeguard
- An action that reduces a threat to an acceptable level.
- Independence in appearance
- Avoiding circumstances that would lead a reasonable third party to doubt objectivity.
- Professional skepticism
- An attitude of a questioning mind and critical assessment of evidence.
- Engagement quality review
- An objective evaluation of significant judgments by a partner outside the engagement team.
- Audit committee
- A committee of independent directors that oversees financial reporting and the auditor.
- NOCLAR
- Non-compliance with laws and regulations, and the professional accountant's response to it.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Name the five fundamental principles.
Show answer
Integrity, objectivity, professional competence and due care, confidentiality, and professional behavior.
Which threat arises when a firm audits a system it designed?
Show answer
A self-review threat.
Rerun the fee program after removing the IT advice. What are total fees and non-audit fees as a share of the audit fee?
Show answer
Total 625; non-audit 240, about 62 percent of the audit fee.
Rerun the rotation program for a partner who started in 2023. What happens?
Show answer
In the range 2023–2027 neither limit is exceeded; under the SEC rule she could not lead the 2028 audit.
Why is a contingent fee prohibited for an audit?
Show answer
It creates a self-interest threat by tying the auditor's pay to the outcome.
What does an engagement quality reviewer do?
Show answer
Objectively evaluates the team's significant judgments and conclusions before the report is released.
Give one example of automation bias in an audit.
Show answer
Accepting a data-analytics or AI tool's output as correct without testing it.
Who pre-approves services for a public-company audit client?
Show answer
The audit committee.
A partner in another office of the firm, not on the team, owns 100 Fairhaven shares. Is that a problem?
Show answer
Generally not, unless she can influence the engagement or works in the engagement partner's office; the firm's policy may be stricter.
What is the difference between independence of mind and in appearance?
Show answer
Mind is actual objectivity; appearance is how a reasonable informed third party would see it.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.