
CISSP-112 · Lesson 9 of 12 · 27 min
Cryptography II: hashing, digital signatures, public key infrastructure and key management
Encryption keeps data secret, but most of what keeps the internet trustworthy is about integrity and identity: knowing that a software update has not been altered, that a website really belongs to your bank, that a contract was signed by the person it claims. This lesson covers the tools for those jobs: hash functions, message authentication codes, digital signatures, the public key infrastructure that binds keys to identities, and the key management practices that keep the whole system working. They complete sub-domain 3.6.
Hash functions
A cryptographic hash function takes input of any length and produces a fixed-length output called a digest, hash or fingerprint. A good hash function has three security properties. Preimage resistance means that given a digest, it is infeasible to find any input that produces it, so hashes are one-way. Second preimage resistance means that given one input, it is infeasible to find a different input with the same digest. Collision resistance means it is infeasible to find any two different inputs with the same digest. A hash also shows the avalanche effect: changing one bit of the input changes about half the bits of the output. Hashing provides integrity, not confidentiality, and uses no key.
MD5, with a 128-bit digest, and SHA-1, with 160 bits, are both broken for collision resistance: practical MD5 collisions were demonstrated in 2004, and Google and CWI Amsterdam published the first practical SHA-1 collision, called SHAttered, in 2017. They must not be used for signatures or certificates. The SHA-2 family, including SHA-256 and SHA-512, is the current workhorse, and SHA-3, standardized in FIPS 202 in 2015 and based on the Keccak design, offers an alternative with a different internal structure. Collision resistance is limited by the birthday paradox: in a group of only 23 people there is about a 50 per cent chance two share a birthday, and similarly an attacker needs only about 2 to the power n over 2 attempts to find a collision in an n-bit hash. That is why a 256-bit hash gives about 128 bits of collision resistance.
import math
# Birthday paradox: chance that at least two of k people share a birthday
k = 23
p_unique = math.prod((365 - i) / 365 for i in range(k))
print(f"{k} people: {1 - p_unique:.1%} chance of a shared birthday")
# Work to find a hash collision is about 2**(n/2)
for n in (128, 160, 256):
print(f"{n}-bit hash: collision work about 2^{n // 2}")23 people: 50.7% chance of a shared birthday 128-bit hash: collision work about 2^64 160-bit hash: collision work about 2^80 256-bit hash: collision work about 2^128
Passwords need special treatment. Storing plain hashes is unsafe, because attackers can use precomputed tables of common passwords, called rainbow tables, or simply guess billions of passwords per second on graphics processors. Password storage should add a unique random salt to each password, so identical passwords produce different hashes and precomputed tables are useless, and should use deliberately slow, memory-hard functions such as Argon2, scrypt, bcrypt or PBKDF2 with a high iteration count. A pepper, a secret value kept separately from the database, can add further protection.
Message authentication codes
A hash alone proves nothing about who created a message, because anyone can compute it. A message authentication code, or MAC, combines the message with a secret key, so only someone holding the key can produce or verify it. HMAC, defined in RFC 2104 and FIPS 198, builds a MAC from a hash function such as SHA-256 and is widely used in protocols and application programming interfaces. Authenticated encryption modes such as GCM build a MAC into encryption. MACs provide integrity and authenticity between parties who share a key, but not nonrepudiation, because either party could have created the MAC.
Digital signatures
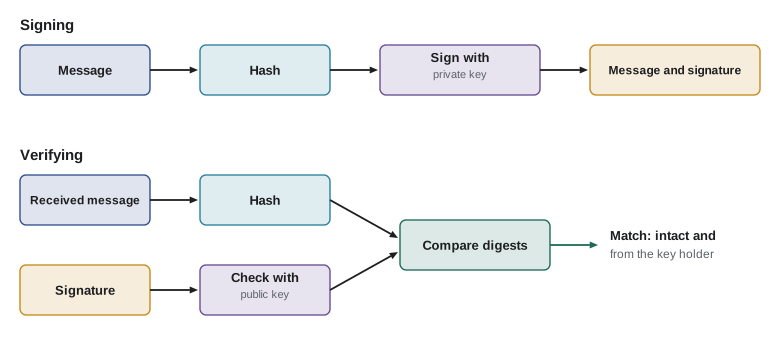
A digital signature provides integrity, authentication of the signer and nonrepudiation. To sign, the sender hashes the message and transforms the digest with their private key. To verify, the recipient hashes the received message, uses the sender's public key to recover or check the signed digest, and compares the two. If they match, the message has not changed and only the holder of the private key could have signed it. Signing does not encrypt the message; if confidentiality is also needed, the message is encrypted separately with the recipient's public key or a session key. Signature algorithms include RSA signatures, the Digital Signature Algorithm, ECDSA and EdDSA, described in FIPS 186-5, and the new post-quantum ML-DSA and SLH-DSA covered in lesson 10.
Nonrepudiation in practice depends on more than mathematics. If a private key is stored on a shared laptop or its password is known to several people, a signer can credibly claim someone else used it. Strong nonrepudiation needs keys held in hardware that only the signer controls, such as a smart card or a security key with a PIN, plus trustworthy timestamps from a time-stamping authority that prove when a signature was made.
Public key infrastructure
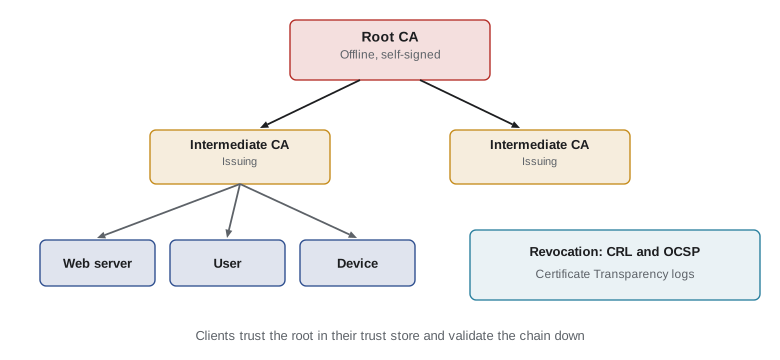
Public keys are only useful if you know whose they are. A public key infrastructure, PKI, binds public keys to identities through digital certificates. A certificate, in the X.509 format, contains the subject's name, public key, validity period, serial number, issuer, permitted key uses and extensions, all signed by a certificate authority, or CA. A registration authority checks the identity of applicants before the CA issues certificates. Trust flows down a chain: a root CA, whose self-signed certificate is installed in operating systems and browsers as a trust anchor, signs certificates for intermediate CAs, which in turn issue end-entity certificates to websites, people and devices. Root keys are kept offline in hardware security modules and used rarely, so that day-to-day issuing happens from intermediates whose compromise is easier to contain.
Certificates sometimes need to be revoked before they expire, for example when a private key is lost. Certificate revocation lists, CRLs, are signed lists of revoked serial numbers published by the CA. The Online Certificate Status Protocol, OCSP, lets a client ask about one certificate in real time, and OCSP stapling lets the server attach a recent signed status to the TLS handshake, which is faster and more private. Because revocation checking has always been unreliable, the industry is moving towards short certificate lifetimes instead. In April 2025 the CA/Browser Forum, which sets rules for publicly trusted TLS certificates, approved a phased reduction of the maximum lifetime: 200 days from 15 March 2026, 100 days from 15 March 2027 and 47 days from 15 March 2029. Automation through the ACME protocol, popularized by Let's Encrypt, is essential at those lifetimes.
Other PKI controls guard against rogue certificates. Certificate Transparency requires publicly trusted CAs to log every TLS certificate in public, append-only logs, so domain owners can spot certificates issued for their names without permission. Certification authority authorization, CAA, DNS records let a domain owner specify which CAs may issue for it. Certificate pinning, where an application accepts only specific keys, can block rogue certificates but makes key changes risky and is now used sparingly. Organizations also run private PKIs for internal servers, Wi-Fi, VPNs, smart card logon and device identity.
Governments run their own PKIs. The Government of Canada operates a PKI for employee credentials, internal systems and secure email, and the Canadian Centre for Cyber Security publishes guidance on cryptographic algorithms in ITSP.40.111 and on PKI practices. Provincial governments and the health sector also run PKIs for digital identity and signatures.
Key management
Key management is where most real cryptographic systems succeed or fail. NIST SP 800-57 describes the key life cycle: generation, using a strong random source, ideally inside a hardware module; registration and distribution, protecting keys in transit and binding them to owners; storage, in HSMs, TPMs or managed key services rather than in code or configuration files; use, restricted to authorized purposes; rotation, replacing keys on a schedule or after suspected compromise; backup and recovery, so encrypted data is not lost; archive; and destruction, securely erasing keys when they are no longer needed, which also makes data encrypted only under them unreadable, a technique called cryptographic erasure.
Several controls protect the most important keys. Split knowledge divides a key into parts so that no single person knows the whole key; dual control requires two or more people to act together, for example to load a master key into an HSM. M of n control, using schemes such as Shamir's secret sharing, lets any 3 of 5 custodians reconstruct a key, so the loss of one or two custodians does not lose the key. Key escrow places a copy of keys with a trusted third party so they can be recovered, for example under legal order; it supports recovery but creates a high-value target and has been controversial when proposed for government access. Keys should have a single purpose, so that the same key is not used for both encryption and signing, and systems should log every use of sensitive keys.
| Tool | Provides | Uses a key? | Example |
|---|---|---|---|
| Hash | Integrity | No | SHA-256 file checksum |
| Salted slow hash | Password protection | No key, but a salt | Argon2, bcrypt |
| MAC or HMAC | Integrity and authenticity between key holders | Shared secret key | HMAC-SHA-256 on API requests |
| Digital signature | Integrity, authenticity, nonrepudiation | Private key to sign, public to verify | Code signing, signed contracts |
| Certificate | Binding of public key to identity | Signed by a CA | X.509 TLS certificate |
Worked problem
Planning for 47-day certificates
An organization manages 1,200 public TLS certificates, renewed by hand once a year at about 20 minutes each. Estimate the yearly effort at today's pace and at a 47-day lifetime, assuming renewal on average every 40 days to leave a safety margin.
Show solution
- Today: 1,200 renewals × 20 minutes = 24,000 minutes, about 400 hours a year.
- At 47-day lifetimes: renewals per certificate per year ≈ 365 / 40 ≈ 9.1.
- Total renewals ≈ 1,200 × 9.1 ≈ 10,950 a year.
- Manual effort ≈ 10,950 × 20 minutes ≈ 219,000 minutes, about 3,650 hours, roughly two full-time staff.
Answer: Manual effort would rise from about 400 to about 3,650 hours a year. Automating issuance and renewal with ACME and a certificate inventory is the only realistic answer.
Worked problem
Verifying a download
A vendor publishes a software update, its SHA-256 hash on the same web page, and a separate digital signature made with the vendor's code-signing key. An attacker who compromised the web server replaced both the file and the hash. Which check catches the attack?
Show solution
- The hash check passes, because the attacker also replaced the published hash.
- The signature check fails, because the attacker does not have the vendor's private key and cannot sign the altered file.
- The client verifies the signature with the vendor's public key from a certificate it already trusts.
Answer: Only the digital signature catches it. A hash published alongside the file proves integrity only if the hash itself comes from a trusted channel.
Thinking like a manager
When a question asks how to prove who sent a message, choose digital signatures; when it asks how two systems sharing a secret can check integrity, choose a MAC; when it asks how to store passwords, choose salted, slow hashing, never encryption. When a CA is compromised, the response is to revoke and replace affected certificates and keys and investigate the trust chain. And for critical keys, think dual control, split knowledge and HSMs.
Common mistakes
MistakeUsing MD5 or SHA-1 for signatures or certificates.
InsteadUse SHA-256 or stronger; MD5 and SHA-1 collisions are practical.
MistakeEncrypting passwords with a reversible key.
InsteadStore passwords with a unique salt and a slow hash such as Argon2 or bcrypt.
MistakeThinking a MAC provides nonrepudiation.
InsteadBoth parties share the MAC key; only signatures give nonrepudiation.
MistakeKeeping the root CA online for daily issuing.
InsteadKeep the root offline in an HSM and issue from intermediates.
MistakeRenewing certificates by hand as lifetimes shrink.
InsteadAutomate with ACME and keep a certificate inventory.
Summary and key terms
- Hash functions give integrity with preimage, second preimage and collision resistance; MD5 and SHA-1 are broken.
- The birthday paradox means collision resistance is about half the digest length.
- Passwords need unique salts and slow, memory-hard hashing.
- MACs such as HMAC give integrity and authenticity between key holders; signatures add nonrepudiation.
- PKI binds keys to identities through X.509 certificates, CAs, registration authorities and trust chains.
- Revocation uses CRLs and OCSP; public TLS certificate lifetimes fall to 47 days by 2029, requiring automation.
- Key management covers generation through destruction, with split knowledge, dual control and HSMs for critical keys.
- Collision resistance
- Infeasibility of finding two inputs with the same hash.
- Birthday attack
- Finding a collision with about 2^(n/2) attempts for an n-bit hash.
- Salt
- A unique random value added to each password before hashing.
- HMAC
- A keyed message authentication code built from a hash function.
- Digital signature
- A value made with a private key that proves integrity and origin.
- Certificate authority
- A trusted entity that signs certificates binding keys to identities.
- OCSP stapling
- Attaching a recent signed revocation status to the TLS handshake.
- Certificate Transparency
- Public logs of issued TLS certificates for detecting misissuance.
- Split knowledge
- Dividing a key so no single person knows all of it.
- Key escrow
- Holding copies of keys with a trusted third party for recovery.
Practice problems
Work each problem on paper first, then reveal the answer to check.
What are the three security properties of a hash function?
Show answer
Preimage resistance, second preimage resistance and collision resistance.
When was a practical SHA-1 collision first published?
Show answer
In 2017, the SHAttered attack.
About how much work does a collision take for a 256-bit hash?
Show answer
About 2^128 operations.
Why salt passwords?
Show answer
So identical passwords hash differently and precomputed tables are useless.
What does an HMAC add to a hash?
Show answer
A secret key, giving authenticity as well as integrity.
Which key verifies a digital signature?
Show answer
The signer's public key.
Who checks applicants' identity before a CA issues certificates?
Show answer
The registration authority.
What is OCSP?
Show answer
The Online Certificate Status Protocol for checking whether a certificate is revoked.
What maximum public TLS certificate lifetime applies from 15 March 2029?
Show answer
47 days.
What is M of n control?
Show answer
Any M of n custodians together can reconstruct or use a key.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.