
CON-260 · Lesson 11 of 12 · 30 min
Digital collaboration, contracts and security
Digital tools change who holds information, who can rely on it and who is responsible when it is wrong or lost. Traditional construction contracts were written around paper drawings and specifications. Models, shared cloud platforms, digital signatures and collaborative delivery methods raise new questions: Is the model a contract document? Who owns the model and can the owner reuse it? Can a contractor rely on model dimensions? What happens if a cyberattack locks the project platform the week before a major pour? This lesson covers collaborative delivery, the contract documents that deal with digital information, intellectual property and reliance, privacy and cybersecurity.
Collaborative delivery and digital information
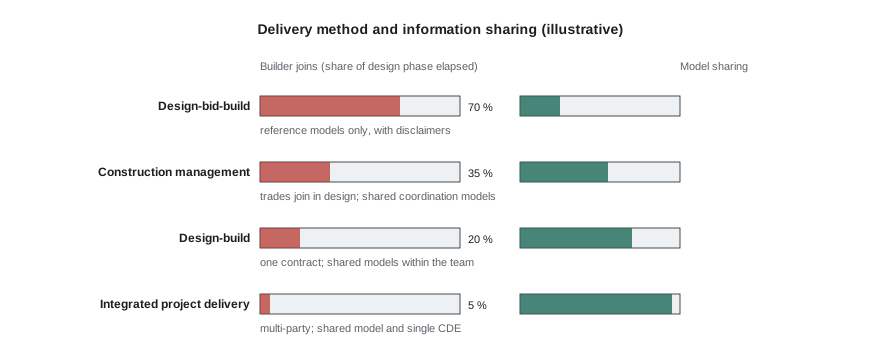
Delivery methods shape how freely information is shared. Under traditional design-bid-build, the designer's model is often not shared with the contractor at all, or shared only as a reference with disclaimers. Construction management, design-build and especially integrated project delivery (IPD) bring the contractor and key trades in early and encourage shared models from the start. IPD uses a multi-party agreement among owner, designer and builder, with shared risk and reward tied to project outcomes, joint decision-making and open books. Digital collaboration is central to it: a shared model, a single CDE, co-located or virtual "big room" coordination and Lean planning.
In the United States, integrated project delivery agreements are available from AIA Contract Documents and ConsensusDocs, and many owners use custom multi-party agreements. These typically include shared risk and reward, a target cost, joint decision-making, open books and limits on claims among the parties. Traditional AIA and ConsensusDocs forms can be adapted for BIM through exhibits and addenda, discussed below.
Contract documents for digital information
A BIM protocol, exhibit or addendum attached to the main contract deals with questions the main contract does not: which models are shared, what each can be used for, the LOD or information requirements at each milestone, who authors each element, whether models are contract documents, how conflicts between models and drawings are resolved, the BIM execution plan, data ownership and licenses, and the security of shared data.
AIA Contract Documents published a suite of digital practice documents in 2022, including E201 and E202 BIM exhibits (with and without designating model versions as contract documents), E401 and E402 exhibits for sharing within the design team or the construction team only, the G203 BIM Execution Plan, G204 and G205 model element tables and the C106 Digital Data Licensing Agreement. ConsensusDocs 301 is a BIM addendum that defines roles, responsibilities and liability for creating and relying on BIM data and includes a standard BIM execution plan.
| Question | Why it matters | Typical contract approach |
|---|---|---|
| Is the model a contract document? | Determines whether model geometry binds the parties | State expressly; often drawings govern unless specific model versions are designated |
| What can each party rely on? | Contractor may build or order from model data | Reliance limited to stated LOD and purpose; verify critical dimensions |
| Who owns the model and data? | Owner may want to reuse for operations or future work | Author keeps copyright; owner receives a license for defined uses |
| What if model and drawings conflict? | Avoids disputes during construction | Order of precedence clause; raise conflicts by RFI |
| Who pays for modeling by trades? | Trades will not model at LOD 350–400 for free | Include in subcontract scope and price |
| How is data secured and retained? | Protects sensitive information and records | Security requirements, access control and export at completion |
Reliance and the standard of care
Designers generally owe a duty to perform their services to the standard of care of a reasonably competent professional; they do not guarantee perfection. When a contractor builds from model data, questions arise about whether it was entitled to rely on that data. Contracts typically limit reliance to the purpose and LOD stated in the model element table: a duct at LOD 300 can be relied on for size and route but not for hanger locations. A contractor that orders steel from a design model it was told was "for information only" may bear the risk of errors itself.
Worked problem
Who bears the risk?
A general contractor receives the structural engineer's model, designated in the BIM exhibit as LOD 300 for coordination only, with drawings governing. The steel fabricator, to save time, generates shop drawings directly from the model without checking against the drawings. One beam elevation in the model is 6 in lower than on the drawings, and 12 beams are fabricated wrong. Who is likely to bear the cost, and what should have happened?
Show solution
- The contract designates the model as for coordination only and states that drawings govern.
- The fabricator relied on the model for fabrication, a use not permitted by the exhibit, and did not check against the governing drawings.
- The cost is therefore likely to fall on the fabricator (and possibly the contractor, depending on the subcontract), not the engineer, although the engineer's model error may also be examined.
- Better practice: the fabricator's detailing model is checked against the drawings and submitted as shop drawings for review; any model-drawing conflict is raised by RFI.
Answer: The party that used the model beyond its permitted purpose without checking usually carries the risk. Clear exhibits, shop drawing review and RFIs prevent the problem.
Intellectual property and licenses
Models, drawings and software are protected by copyright. In general, the author of a work owns the copyright unless a contract assigns it. Design contracts usually leave copyright with the designer and grant the owner a license to use the documents for the project, and sometimes for operation, maintenance and future alterations. Owners who want to reuse models for facility management, or to give them to a future contractor, should make sure the license covers those uses. Trade models, fabrication data and proprietary families or objects may belong to the trades and suppliers who created them and need their own license terms.
Software licenses matter too. Project platforms are usually licensed by subscription; when the subscription ends, access may end. Contracts should require that project records be exportable in usable formats (PDF, IFC, BCF, CSV and native files where agreed) and handed over or retained for the required period. An owner who receives only a link to a platform that will be switched off has not received the record.
Digital signatures, seals and records
Electronic signatures and digital seals are now widely accepted. The federal E-SIGN Act and state laws based on the Uniform Electronic Transactions Act give legal effect to electronic signatures and records, and state licensing boards set rules for digital seals on engineering and architectural documents. Contracts should say how documents are signed and issued and which digital version is the official record.
Record retention requirements depend on the contract, the owner and the law. Limitation periods for claims and statutory requirements for some documents mean that many project records should be kept for years after completion. The CDE and field platform archives (Lessons 4 and 7) should be designed for this from the start.
Privacy
Construction projects collect personal information: workers' names, contact details, certifications, timesheets, injury reports, photos and video, location data from badges and telematics, and sometimes biometric data from site access systems. Privacy law applies to these data.
In the United States there is no general federal private-sector privacy law. About twenty states have enacted comprehensive consumer privacy laws, starting with California's CCPA as amended by the CPRA, which notably applies to employee and job-applicant data as well. Illinois' Biometric Information Privacy Act requires written consent before collecting biometric identifiers such as fingerprints or face geometry, and has produced large class-action settlements, which matters for biometric site-access systems. Sector-specific federal laws and state breach-notification laws in every state also apply.
Practical steps include collecting only the personal information needed, telling workers what is collected and why, limiting access, setting retention periods, securing the data and choosing vendors who meet these obligations. Site cameras and 360-degree captures (Lesson 8) need particular care because they record images of people who may not expect it.
Cybersecurity
Construction has become a frequent target of cyberattacks. Contractors handle large payments, work with many small partners whose security may be weak, rely on cloud platforms and email for urgent instructions, and often have limited IT staff. Threat research published in late 2025 ranked construction among the three most-attacked sectors for ransomware in 2025, with most victims in the United States and Canada. Common attacks include phishing that steals platform credentials, business email compromise that diverts payments to fraudulent bank accounts, ransomware that encrypts project files and backups, and data theft from shared platforms.
Worked problem
Business email compromise
A project accountant receives an email that appears to come from a regular concrete supplier, saying its bank has changed and attaching new banking details for the $486,000 progress payment due Friday. The email address differs from the usual one by a single letter. What controls should prevent the payment from being diverted?
Show solution
- Treat any change of banking details as high risk, whatever the email looks like.
- Verify by calling the supplier on a phone number already on file, not one given in the email.
- Require a second person to approve changes to vendor banking details.
- Train staff to spot look-alike addresses and urgency pressure, and report suspicious emails.
Answer: Out-of-band verification and dual approval of banking changes would stop this fraud, regardless of how convincing the email is.
A practical cybersecurity program for a contractor rests on a few basics: multi-factor authentication on email and every project platform; prompt updates of software and devices; least-privilege access (people see only what they need) and removing access when people leave a project; offline or immutable backups tested by restoring them; staff training on phishing and payment fraud; an incident response plan with contacts; and security requirements for subcontractors and vendors. Cyber insurance is common but increasingly requires these controls.
Worked problem
Scoring cyber risks
A contractor rates four risks for a hospital project on likelihood (1–5) and impact (1–5). Phishing that steals platform credentials: likelihood 4, impact 4. Ransomware encrypting project files: 3, 5. Loss of a field tablet with offline drawings: 4, 2. Leak of the hospital's security-sensitive layouts: 2, 5. Rank the risks by score (likelihood × impact) and suggest one control for each.
Show solution
- Phishing credentials: 4 × 4 = 16; control: multi-factor authentication on all platforms.
- Ransomware: 3 × 5 = 15; control: tested offline or immutable backups and patching.
- Sensitive layout leak: 2 × 5 = 10; control: restricted access and ISO 19650-5 security-minded handling.
- Lost tablet: 4 × 2 = 8; control: device encryption and remote wipe.
Answer: Rank: phishing (16), ransomware (15), sensitive layout leak (10), lost tablet (8). Scores guide where to spend first, while high-impact risks deserve attention even at lower likelihood.
Some projects carry specific security obligations. Defense contractors handling controlled unclassified information must meet the Cybersecurity Maturity Model Certification (CMMC) requirements, which began a phased rollout in Department of Defense contracts on 10 November 2025. Other federal agencies impose NIST-based requirements, and owners of sensitive assets may require security-minded information management following ISO 19650-5. Contractors on critical infrastructure projects should expect security requirements passed down by contract.
Security-minded information management
ISO 19650-5 asks the owner to assess whether information about an asset could be used to cause harm, for example by revealing the layout of a data center, the security systems of a courthouse or the vulnerabilities of a water treatment plant. If so, a security management plan sets rules for who may access which information, how it is marked, stored, shared and disposed of, and how breaches are handled. On such projects, publishing detailed models or site photos on social media, a common marketing habit, may be prohibited.
Putting it together
For a construction manager, the practical message is to make digital collaboration explicit in the contract: name the models and their permitted uses, attach a BIM execution plan, state the order of precedence, make modeling part of subcontract scopes, secure licenses for owner reuse, plan record retention and export, protect personal information and build basic cybersecurity into every project. Most digital disputes arise not from technology failing but from assumptions nobody wrote down.
Common mistakes
MistakeAssuming the model governs because it is the most detailed information.
InsteadState in the contract whether models are contract documents and which governs in a conflict.
MistakeFabricating directly from a design model marked for coordination only.
InsteadUse models only for permitted purposes; check against governing documents and submit shop drawings.
MistakeAssuming the owner owns the model because it paid for it.
InsteadCheck the license terms and secure rights for operation, maintenance and reuse.
MistakeChanging vendor bank details on the strength of an email.
InsteadVerify changes by phone using known numbers and require dual approval.
MistakeRelying on cloud platforms without tested backups.
InsteadKeep offline or immutable backups and test restoration regularly.
Summary and key terms
- Delivery methods shape information sharing; IPD relies on shared models and joint decisions.
- BIM exhibits, addenda or appendices define model uses, LOD, authorship, precedence and data rights.
- Reliance on model data is limited to the stated purpose and LOD; using models beyond that shifts risk.
- Authors usually keep copyright; owners need licenses for reuse; records must be exportable.
- Electronic signatures and digital seals are legally recognized when requirements are met.
- Privacy law applies to workers' personal information, images and biometrics, and differs between Canada and the US.
- Construction is a frequent cyber target; MFA, backups, training and payment controls are basic defenses.
- Sensitive assets need security-minded information management under ISO 19650-5.
- Integrated project delivery (IPD)
- A delivery method using a multi-party agreement with shared risk and reward.
- BIM exhibit
- A contract attachment defining how models are shared and used.
- Order of precedence
- A clause stating which document governs when documents conflict.
- Standard of care
- The level of skill and care expected of a reasonably competent professional.
- Reliance
- A party's entitlement to use information as accurate for a purpose.
- License
- Permission to use a work without owning its copyright.
- Business email compromise
- Fraud using spoofed or hijacked email, often to divert payments.
- Ransomware
- Malicious software that encrypts data and demands payment.
- Multi-factor authentication (MFA)
- Login requiring two or more forms of verification.
- Security-minded information management
- Controls on sensitive asset information under ISO 19650-5.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Name three features of IPD.
Show answer
Multi-party agreement, shared risk and reward, joint decision-making, open books, early involvement, shared model.
What should a BIM exhibit say about models and drawings?
Show answer
Whether models are contract documents and which governs in a conflict.
Who usually owns copyright in a design model?
Show answer
The author (designer), unless the contract assigns it; the owner gets a license.
Why should project records be exportable?
Show answer
Platform access may end with the subscription; the record must survive.
A risk has likelihood 3 and impact 4. What is its score?
Show answer
12.
Name four basic cybersecurity controls for a contractor.
Show answer
MFA, patching, least-privilege access, tested backups, training, incident response plan, vendor requirements.
How should a request to change supplier bank details be handled?
Show answer
Verify by phone using a known number and require dual approval.
What does ISO 19650-5 address?
Show answer
Security-minded information management for sensitive assets.
Why are biometric site-access systems a privacy concern?
Show answer
Biometric data are sensitive and some laws require consent and strict handling.
What usually causes digital disputes?
Show answer
Unwritten assumptions about model status, reliance, ownership and responsibilities.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.