
WEB-230 · Lesson 11 of 12 · 24 min
Privacy by design and handling personal data
▶ Video coming soon A video version of this lesson is on the way.
On Tuesday, February 20, Dev and Lucy join the session, because privacy is as much about decisions as about code. Lucy keeps the volunteer records; Dev sends the newsletters and runs the youth garden's sign-up each spring. Theo starts by putting a single number on the board: 41. It is the number of separate pieces of information the PHP application stores about each volunteer, counting every field in every table that links to a volunteer's id. "How many of these do we actually use?" he asks. Lucy reads down the list and stops at twenty-two.
That gap is what this lesson is about. Personal information is any information about an identifiable person: a name, an e-mail address, a phone number, but also availability, dietary needs, the agency someone visits, an IP address in a log, or a combination of details that together point to one person. Collecting it creates obligations and risks. Every field stored is a field that can leak, be misused, be requested, or have to be corrected or deleted. The cheapest personal information to protect is the information you never collected.
Privacy by design
Privacy by design is a set of principles developed in the 1990s by Ann Cavoukian, then Ontario's Information and Privacy Commissioner, and since adopted by privacy regulators around the world and written into laws such as Europe's GDPR. Its seven principles are short enough to keep on a card.
| Principle | What it means for the Food Hub |
|---|---|
| Proactive, not reactive | Think about privacy when designing a feature, not after a complaint |
| Privacy as the default | Collect the minimum and share nothing unless a person chooses to |
| Privacy embedded into design | Build it into data models, forms and logs, not as an add-on |
| Full functionality | Privacy and usefulness together, not one traded for the other |
| End-to-end security | Protect data for its whole life, from collection to deletion |
| Visibility and transparency | Say clearly what is collected and why, and keep that promise |
| Respect for the user | Make choices easy, defaults kind and requests easy to make |
The most practical of the seven is privacy as the default, which in day-to-day work becomes data minimization: collect only what a feature needs, keep it only as long as it is needed, and show it only to people who need it. Theo's example from the review is the portal's shift export, finding F1 from lesson 2. It gave every volunteer on a shift the phone numbers of everyone else on it. The intention was kind, so that volunteers could call each other about lifts, but nobody had asked the volunteers. The fix is to show first names only, and to let volunteers opt in to sharing a number.
// Data minimization: compare what is collected with what each purpose needs.
const collected = ['name', 'email', 'phone', 'birthDate', 'address', 'areas', 'availability', 'dietaryNeeds', 'emergencyContact', 'howHeard', 'employer'];
const purposes = {
  'schedule shifts': ['name', 'email', 'areas', 'availability'],
  'reminders and changes': ['email', 'phone'],
  'kitchen safety': ['dietaryNeeds', 'emergencyContact'],
  'youth garden (under 18 needs consent)': ['birthDate'],
};

const needed = new Set(Object.values(purposes).flat());
const unneeded = collected.filter((f) => !needed.has(f));
console.log('needed by a purpose:', [...needed].sort().join(', '));
console.log('collected with no purpose:', unneeded.join(', ') || 'none');
console.log(`${unneeded.length} of ${collected.length} fields can be dropped from the form`);needed by a purpose: areas, availability, birthDate, dietaryNeeds, email, emergencyContact, name, phone collected with no purpose: address, howHeard, employer 3 of 11 fields can be dropped from the form
What this code does
Each purpose lists the fields it truly needs, and the union of those lists is everything the Food Hub can justify collecting. Any field collected but not needed by a purpose is a candidate for removal. Writing purposes down this way also answers the question privacy law asks first: why do you have this?
The law, briefly
Privacy law differs between the two countries, and Theo is careful to say that the studio does not give legal advice; the Food Hub's own lawyer and its board decide how the law applies. What the studio can do is build software that makes compliance easy and keeps the promises the Food Hub makes.
In the United States, there is no general federal privacy law. Wisconsin, where the Food Hub is based, has no comprehensive consumer privacy law; bills to create one did not pass in March 2026. About two dozen states had such laws by the middle of 2026, and several of them, though not all, exempt non-profits; Wisconsin's breach notification law still requires telling people when certain personal information is exposed. One federal law matters directly: the Children's Online Privacy Protection Act (COPPA) applies to online services that collect personal information from children under 13, and the youth garden's online sign-up asks for a child's name and age. The FTC's amended COPPA Rule, published in April 2025 with compliance required by April 22, 2026, tightened consent and data retention rules. The Food Hub's approach is to have parents sign children up and to collect nothing from the children themselves. E-mail newsletters follow CAN-SPAM, which requires an opt-out honored within 10 business days.
Whatever the law in a given place, the same practices satisfy most of it: know what you collect and why, ask clearly, keep data secure, keep it no longer than needed, let people see and correct it, and tell them if something goes wrong. Those are engineering tasks as much as legal ones.
Consent and transparency
Where consent is the basis for using data, it must be meaningful: the person understands what they are agreeing to, the request is separate from other terms, and saying no is as easy as saying yes. In practice that means a short, plain-language notice at the point of collection, saying what the information will be used for, and unticked checkboxes for anything optional, such as the newsletter or sharing a phone number with other volunteers. Consent should be recorded with what was agreed to, when, and the wording shown, so the Food Hub can prove it later, and withdrawing it should take one click.
<fieldset>
  <legend>Optional</legend>
  <label><input type="checkbox" name="newsletter"> Send me the monthly volunteer newsletter</label>
  <label><input type="checkbox" name="sharePhone"> Share my phone number with others on my shifts, so we can arrange lifts</label>
</fieldset>
<p class="hint">We use your details only to schedule shifts and contact you about them.
  <a href="/privacy">How we handle your information</a></p>
What this code does
Both optional uses are unticked checkboxes with plain labels, so the default is to share nothing. The hint says what the required details are for at the moment they are collected, and links to the full notice. The same markup is accessible too, because each checkbox has a real label and the group has a legend.
Keeping personal data out of places it does not belong
Personal data spreads. It ends up in logs, error reports, analytics, backups, spreadsheets exported for a meeting, and e-mails. JS-260 set the rule that logs record ids and chosen fields, never secrets or personal details. The review checks that the rule is followed, and adds a redaction step for free text, where people type phone numbers and e-mail addresses into notes and messages that may be logged or sent to an error tracker.
// Redact e-mail addresses and North American phone numbers from free text before logging.
const EMAIL = /[A-Za-z0-9._%+-]+@[A-Za-z0-9.-]+\.[A-Za-z]{2,}/g;
const PHONE = /(?:\+?1[\s.-]?)?\(?\d{3}\)?[\s.-]?\d{3}[\s.-]?\d{4}\b/g;

function redact(text) {
  return text.replace(EMAIL, '[email]').replace(PHONE, '[phone]');
}

const notes = [
  'Please call Joan at (608) 555-0183 if the trays are late.',
  'New contact is priya.s@westview.example, backup 613.555.0142',
  'Order 418: 6 trays, no nuts',
];
for (const n of notes) console.log(redact(n));Please call Joan at [phone] if the trays are late. New contact is [email], backup [phone] Order 418: 6 trays, no nuts
What this code does
Two regular expressions match e-mail addresses and ten-digit phone numbers written in the usual ways, with or without a country code, brackets, dots or dashes. Each match is replaced with a placeholder that shows what kind of detail was removed. The order note has nothing personal in it and passes through unchanged, so the log stays useful.
Sometimes a system needs to tell records apart without knowing who they belong to: counting how many distinct volunteers used the portal this month, for example. Pseudonymization replaces an identifier with a consistent value that cannot be reversed without a secret. An HMAC of the volunteer id with a key kept outside the analytics system works well: the same volunteer always gives the same value, but someone with the analytics data alone cannot work back to the id. Pseudonymized data is still personal data, because whoever holds the key can link it, but it is far less risky to share.
// Pseudonymize volunteer ids for usage statistics with a keyed HMAC.
const enc = new TextEncoder();
const key = await crypto.subtle.importKey('raw', enc.encode('analytics-key-kept-elsewhere'), { name: 'HMAC', hash: 'SHA-256' }, false, ['sign']);
const pseudo = async (id) => [...new Uint8Array(await crypto.subtle.sign('HMAC', key, enc.encode(`volunteer:${id}`)))]
  .slice(0, 6).map((b) => b.toString(16).padStart(2, '0')).join('');

const visits = [1042, 877, 1042, 1500, 877, 1042];
const tokens = await Promise.all(visits.map(pseudo));
console.log(tokens.join(' '));
console.log('distinct volunteers:', new Set(tokens).size, 'from', visits.length, 'visits');e0d5a6b53ea9 1a45282bbb71 e0d5a6b53ea9 94bd631623ac 1a45282bbb71 e0d5a6b53ea9 distinct volunteers: 3 from 6 visits
What this code does
Each volunteer id is signed with a key that the analytics system never sees, and the first six bytes of the result become the pseudonym. The same id always produces the same pseudonym, so distinct visitors can still be counted. Without the key, nobody can turn a pseudonym back into a volunteer id or check a guess.
Retention and deletion
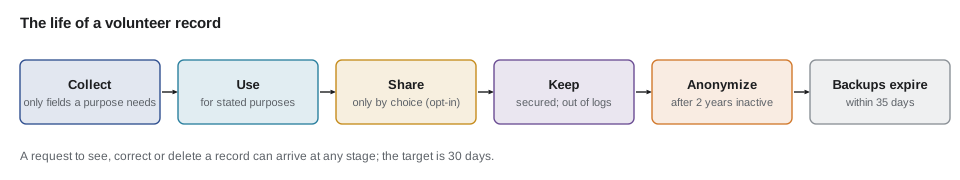
Keeping data forever is the default in most systems, and it is the opposite of what privacy law expects. A retention schedule says how long each kind of record is kept and what happens then: deletion, or anonymization, which removes the details that identify a person while keeping numbers that are useful. In November 2026, Mira drafted the Food Hub's rules during WEB-201: volunteer records inactive for two years are anonymized, removal requests are acted on within 30 days, and backups are kept 35 days, so a deleted record is gone from backups within five weeks. Paul's board approved them in 2027. The review checks that the code does what the schedule says, and finds that the anonymization job was written but never scheduled. That is finding F10.
// When is each volunteer record due for anonymization? (inactive for two years)
const day = (s) => Date.UTC(+s.slice(0, 4), +s.slice(5, 7) - 1, +s.slice(8, 10));
const fmt = (t) => new Date(t).toISOString().slice(0, 10);
const addYears = (s, n) => fmt(Date.UTC(+s.slice(0, 4) + n, +s.slice(5, 7) - 1, +s.slice(8, 10)));

const today = '2029-02-20';
const volunteers = [
  { id: 1042, lastActive: '2028-12-16' },
  { id: 655, lastActive: '2026-11-07' },
  { id: 731, lastActive: '2027-02-20' },
  { id: 908, lastActive: '2027-03-02' },
];

for (const v of volunteers) {
  const due = addYears(v.lastActive, 2);
  const status = day(due) <= day(today) ? 'anonymize now' : `due ${due}`;
  console.log(String(v.id).padStart(4), v.lastActive, '->', status);
}1042 2028-12-16 -> due 2030-12-16 655 2026-11-07 -> anonymize now 731 2027-02-20 -> anonymize now 908 2027-03-02 -> due 2029-03-02
What this code does
The due date is two calendar years after the last activity, worked out by adding to the year rather than counting days, so leap years cannot shift it. Records whose due date is today or earlier are anonymized now, including the one that falls exactly on today. Using fixed dates rather than the clock keeps the example repeatable.
Deletion also has to reach every copy: the database, search indexes, exported spreadsheets, the mail service's contact list and the error tracker. A data inventory, a list of every place personal data lives, is what makes that possible, and it is the same list a breach response needs. Mira builds the inventory as a table in the review report: system, data held, purpose, who can see it, retention, and how deletion reaches it.
Requests and breaches
People have the right to ask what information an organization holds about them and to have it corrected, and in many places deleted. The portal now has a page where a volunteer can download their own record as a file and ask for corrections or deletion, which reaches Lucy's queue with a 30-day target. Building this as a feature, rather than handling requests by hand, is what makes the deadline achievable.
And if personal data is exposed, the clock starts. The Food Hub's breach plan, written with the review, names who decides, who is told, and how quickly: the studio tells Paul within 24 hours of finding a suspected breach, the Food Hub assesses the risk of harm, and then reports and notifies as the law requires. The logs, inventory and access records built throughout this course are what let the team answer the first questions in any breach: what was exposed, whose, and since when.
Worked problem
How much smaller is the sign-up form?
The volunteer sign-up form has 14 fields. Lucy and Theo agree to remove 4 that no purpose needs (address, employer, how heard, birth date for adults) and to make 2 more optional (phone and emergency contact for volunteers who never work in the kitchen). Each removed or optional field takes a volunteer about 8 seconds to fill in. With 300 sign-ups a year, how many fields remain required, and how much volunteer time is saved each year if every optional field is skipped?
Show solution
- Required fields after the change: 14 − 4 removed − 2 now optional = 8.
- Fields no longer filled in per sign-up: 4 + 2 = 6.
- Time saved per sign-up: 6 × 8 = 48 seconds.
- Per year: 300 × 48 = 14,400 seconds, or 14,400 ÷ 3,600 = 4 hours.
Answer: Eight fields remain required, and volunteers save about four hours a year in total. The bigger saving is that four kinds of personal data are no longer stored at all.
Common mistakes
MistakeCollecting a field because it might be useful one day.
InsteadCollect only what a stated purpose needs, and remove the rest.
MistakePre-ticking consent boxes or bundling consent with terms.
InsteadAsk separately, in plain language, with unticked boxes, and record what was agreed.
MistakeWriting personal details into logs and error reports.
InsteadLog ids and chosen fields, redact free text, and scrub error reports.
MistakeKeeping records forever.
InsteadFollow a retention schedule, schedule the deletion or anonymization job, and make sure backups expire.
MistakeHandling access and deletion requests by hand with no record.
InsteadBuild a request feature with a deadline, and keep an inventory so deletion reaches every copy.
Summary and key terms
- Personal information is any information about an identifiable person, and every field stored creates risk and obligations.
- Privacy by design, developed by Ontario's former Privacy Commissioner, asks for privacy to be proactive, the default, embedded, compatible with functionality, secure end to end, transparent and respectful; in practice that means data minimization. In the United States there is no general federal law and Wisconsin has none of its own, but COPPA governs data from children under 13 and state breach laws apply. Consent must be meaningful and recorded, personal data kept out of logs through redaction, pseudonymization used for statistics, and a retention schedule enforced in code, with requests and breaches planned for.
- Personal information
- Any information about an identifiable person, including combinations of details that point to one person.
- Privacy by design
- Seven principles for building privacy into systems from the start, developed by Ann Cavoukian.
- Data minimization
- Collecting, keeping and showing only the personal information a purpose needs.
- Meaningful consent
- Agreement given by a person who understands what they agree to, with refusal as easy as acceptance.
- Redaction
- Removing or replacing personal details in text before it is stored, logged or shared.
- Pseudonymization
- Replacing an identifier with a consistent value that cannot be linked back without a separate secret.
- Retention schedule
- Rules saying how long each kind of record is kept and what happens to it afterwards.
- Data inventory
- A list of every system that holds personal information, what it holds and why.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Why is the cheapest personal information to protect the information you never collect?
Show answer
It cannot leak, be misused or need correcting or deleting.
Is pseudonymized data still personal data?
Show answer
Yes, because whoever holds the key can link it back to a person; it is lower risk, not risk-free.
Why add two years to the year rather than 730 days for the retention date?
Show answer
So leap years do not shift the date.
What does a data inventory make possible?
Show answer
Deletion that reaches every copy, and quick answers about what was exposed in a breach.
Try it yourself
Redact contact details
Complete redact(text) so that e-mail addresses become [email] and ten-digit phone numbers written as (613) 555-0142, 613-555-0142, 613.555.0142 or 6135550142 become [phone].
Other numbers, such as order numbers, must not change.
function redact(text) {
  return text;
}

console.log(redact('Call (613) 555-0142 or 608.555.0183 after 3.'));
console.log(redact('Contact lucy@riverside-food-hub.example about order 418.'));
console.log(redact('Text 6135550199, 6 trays.'));
Try it yourself
Retention due date
Complete dueDate(lastActive, years) so that it returns the date years calendar years after lastActive, as YYYY-MM-DD. Both dates are strings like 2027-03-02.
Then isDue(lastActive, today) should return true when the two-year due date is on or before today.
function dueDate(lastActive, years) {
  return lastActive;
}

function isDue(lastActive, today) {
  return false;
}

console.log(dueDate('2027-03-02', 2), dueDate('2026-11-07', 2));
console.log(isDue('2027-02-20', '2029-02-20'), isDue('2027-03-02', '2029-02-20'));
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.