
NUC-410 · Lesson 1 of 12 · 21 min
Safety principles and defense in depth
Hana Okoye's final rotation at Meridian Nuclear Engineering is with the safety analysis group. Its lead, Dr. Lise Fortin, has spent twenty years writing and reviewing safety analysis reports for pressurized water reactors. On Hana's first day she puts a binder on the desk: the updated final safety analysis report for one of TVA's PWR units, several thousand pages long. "Everything you learned in physics, thermal hydraulics, materials and systems ends up here," Lise says. "This document is the argument that the plant is safe. Over the next three months you will learn how that argument is built, how it is tested, and what the accidents at Three Mile Island, Chernobyl and Fukushima taught us about where it can fail."
What nuclear safety means
The fundamental safety objective, as the International Atomic Energy Agency states it, is to protect people and the environment from the harmful effects of ionizing radiation. For a power reactor, almost all of the potential for harm lies in the inventory of radioactive fission products in the fuel. A large reactor that has run for a year holds a quantity of radioactive material far greater than anything else in industry, and it keeps producing heat from radioactive decay for months after it is shut down. Nuclear safety is the set of design features, procedures and organizational practices that keep that material where it belongs under all conditions: in normal operation, during equipment failures and in accidents.
Three safety functions must be maintained at all times. The first is to control reactivity: the chain reaction must be stopped when needed and kept stopped. The second is to cool the fuel, including the decay heat after shutdown. The third is to confine radioactive material, so that it does not escape even if the first two functions are partly lost. Almost every safety system in a plant serves one of these three functions, and almost every serious accident involves the loss of one or more of them. A useful habit for any safety engineer is to ask, for every event, which of the three functions is challenged and what still protects it.
| Safety function | Normal means | Backup means | Typical challenge |
|---|---|---|---|
| Control reactivity | control rods or absorbers, soluble boron, zone controllers | independent shutdown systems, emergency boration, poison injection | failure to trip after a transient |
| Cool the fuel | main coolant pumps and steam generators | emergency core cooling, auxiliary feedwater, passive cooling | loss of coolant, loss of power |
| Confine radioactive material | fuel matrix, cladding, pressure boundary | containment, isolation valves, filtered venting | containment bypass, overpressure, hydrogen |
Defense in depth
No design is perfect, no equipment is perfectly reliable and no person is free of error. The central idea of reactor safety is therefore not to rely on any single feature. Defense in depth means providing several independent layers of protection, so that if one fails another still works. The concept has two parts that are often confused. The first is a set of physical barriers between the fission products and the public. The second is a set of levels of protection, each of which aims to prevent the failure of the barriers or to limit the consequences if they fail.
The physical barriers in a water-cooled reactor are the ceramic fuel matrix, which holds most fission products inside its grains; the fuel cladding, a sealed zirconium alloy tube; the reactor coolant pressure boundary, made of the vessel or pressure tubes, piping and steam generator tubes; and the containment building. A release to the environment requires all four to fail or to be bypassed. Each barrier has limits that analysis must show are respected: fuel temperatures below melting, cladding temperatures and oxidation within acceptance criteria, pressure boundary stresses within code allowables, and containment pressure below its design value.
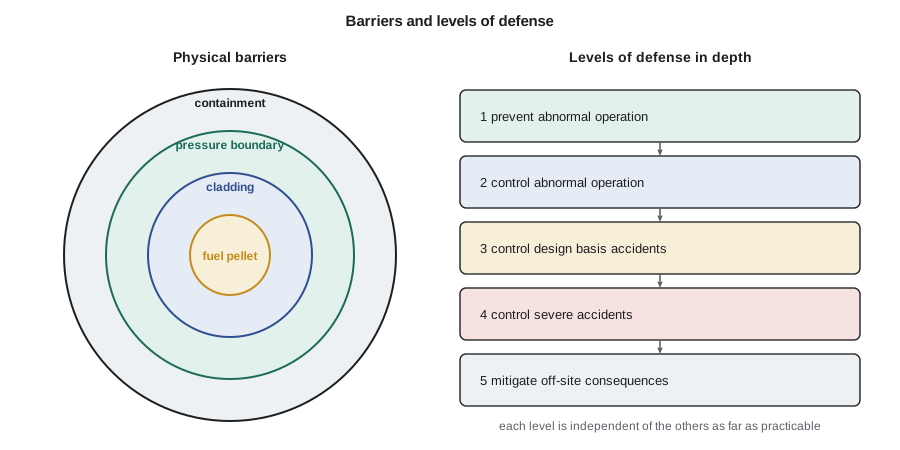
The IAEA describes five levels of defense. Level 1 is the prevention of abnormal operation and failures, through conservative design, high-quality construction and good operation. Level 2 is the control of abnormal operation and the detection of failures, through control and limiting systems and surveillance. Level 3 is the control of accidents within the design basis, through engineered safety features and accident procedures. Level 4 is the control of severe conditions, including preventing the progression of accidents and mitigating severe accidents, through accident management and containment protection. Level 5 is the mitigation of the radiological consequences of significant releases, through off-site emergency response.
The levels are meant to be independent. A failure that defeats one level should not also defeat the next. In practice this independence is the hardest part to achieve, and many serious events have involved a single cause that cut across several levels at once. At Fukushima Daiichi, the tsunami disabled normal power (level 2), the emergency diesel generators and switchgear (level 3) and much of the equipment that operators needed for accident management (level 4) in the same few minutes. The lesson is not that defense in depth failed as an idea, but that the independence between levels had been assumed rather than demonstrated for that hazard.
# Defense in depth as a chain of independent barriers (illustrative probabilities).
# A release needs every barrier to fail. If the failures are independent, the
# probabilities multiply. A shared cause (one event that defeats two barriers) breaks this.
barriers = [
    ("fuel pellet and cladding damaged", 1e-2),
    ("pressure boundary breached", 1e-1),
    ("containment fails or is bypassed", 1e-2),
]
initiator = 1e-2   # per reactor-year: an event that challenges the barriers
p = 1.0
for name, pf in barriers:
    p *= pf
    print(f"{name:34s} conditional failure probability {pf:.0e}")
print(f"release frequency if independent: {initiator * p:.1e} per reactor-year")
# Now suppose one external event (a large flood) defeats both the cooling and the
# containment function together with probability 0.05 given the flood.
flood = 1e-4      # per reactor-year
common = 0.05
print(f"release frequency from the shared-cause flood: {flood * common:.1e} per reactor-year")
print("the shared cause dominates: independence matters more than the number of barriers")fuel pellet and cladding damaged conditional failure probability 1e-02 pressure boundary breached conditional failure probability 1e-01 containment fails or is bypassed conditional failure probability 1e-02 release frequency if independent: 1.0e-07 per reactor-year release frequency from the shared-cause flood: 5.0e-06 per reactor-year the shared cause dominates: independence matters more than the number of barriers
The program shows the arithmetic behind the idea. Three barriers that each fail with a conditional probability of one in a hundred or one in ten give a release frequency of one in ten million per year if they are truly independent. A single flood that defeats cooling and containment together, even at a low frequency, gives a release frequency fifty times higher. Adding more barriers of the same kind does nothing about the shared cause. Removing the shared cause, by siting, by protecting equipment or by providing diverse backups that the flood cannot reach, is what reduces the risk.
Design principles that support defense in depth
Several design principles make the levels of defense real. Redundancy means providing more equipment than the minimum needed, so that a single failure does not disable a safety function. Most safety systems have two or more independent trains, each able to do the job alone. Diversity means using different types of equipment, or different physical principles, to perform the same function, so that a design error or common environmental stress does not disable all trains. Examples are a second shutdown system that uses liquid poison instead of rods, or a turbine-driven pump alongside motor-driven pumps. Physical separation means placing redundant trains in different rooms or fire areas, so that a fire, flood or pipe whip does not affect more than one.
The single-failure criterion requires that a safety system be able to perform its function even with any single active failure, in addition to the event that caused the demand. Fail-safe design means that a component fails into a safe state, for example control rods that drop into the core by gravity when power to their holding mechanisms is lost. Conservative design margins, such as operating fuel well below its melting point and designing pressure components with ample allowances, give room for uncertainty. Inherent and passive features, such as negative temperature coefficients of reactivity or natural circulation cooling, reduce reliance on equipment that must start and run.
| Principle | Meaning | Example |
|---|---|---|
| Redundancy | more trains than needed | four 50 percent emergency injection trains |
| Diversity | different kinds of equipment for the same function | shutdown rods and liquid poison injection |
| Separation | trains in separate areas | fire-rated walls between electrical divisions |
| Single-failure criterion | function survives any one active failure | two-train system still works with one pump failed |
| Fail-safe | failure leads to a safe state | rods drop on loss of power |
| Passive features | no pumps or power needed | gravity-driven water, natural circulation |
Safety requirements and the licensing basis
In the United States, the Atomic Energy Act and the NRC's regulations in Title 10 of the Code of Federal Regulations set the legal framework. Part 50 contains the General Design Criteria in Appendix A, which require, among other things, redundancy, separation, emergency core cooling and containment, and the emergency core cooling acceptance criteria in 10 CFR 50.46. Part 52 provides for design certification and combined licenses. The licensee's updated final safety analysis report demonstrates that the plant meets these requirements, and the NRC reviews it. Lessons 3 and 6 look at the deterministic and probabilistic analyzes in detail.
The licensing basis is the set of requirements, analyzes and commitments that a plant must continue to meet. It is not fixed at the start of operation. Plants are inspected continually, events are reported and analyzed, and periodic reviews compare the plant against current standards. When new knowledge appears, such as a better understanding of a hazard or a lesson from an accident elsewhere, regulators can require changes. After Fukushima, regulators in many countries required new equipment and strategies at existing plants, as lesson 11 describes.
Safety goals
Defense in depth tells designers how to build a safe plant, but it does not say how safe is safe enough. Safety goals answer that question in quantitative terms. They are usually stated as frequencies of core damage and of large releases, or as limits on the added risk to an individual living near the plant. Probabilistic safety assessment, the subject of lesson 6, estimates these frequencies for a specific plant so that they can be compared with the goals.
The NRC's 1986 Safety Goal Policy Statement sets qualitative goals and two quantitative health objectives: the added risk of prompt fatality to an average individual near the plant, and the added risk of cancer fatality to the population nearby, should each be less than one tenth of one percent of the risk from other causes. In practice the NRC uses surrogate measures: a core damage frequency of about one in ten thousand reactor-years and a large early release frequency of about one in a hundred thousand. Lesson 6 explains how these numbers are estimated and used in risk-informed decisions.
Worked problem
Checking a barrier argument
An initiating event occurs about once in 100 years. Given the event, the probability that emergency cooling fails is 1 × 10⁻³, and given that, the probability that containment fails is 1 × 10⁻¹. What is the large release frequency if the failures are independent?
Show solution
- Initiating event frequency: 1 × 10⁻² per year.
- Core damage frequency from this event: 1 × 10⁻² × 1 × 10⁻³ = 1 × 10⁻⁵ per year.
- Large release frequency: 1 × 10⁻⁵ × 1 × 10⁻¹ = 1 × 10⁻⁶ per year.
Answer: The large release frequency is about one in a million per reactor-year, provided the three failures share no common cause.
Safety is also organizational
Hardware is only part of defense in depth. Procedures, training, maintenance, quality assurance and the attitudes of the people who run the plant are layers too. The accidents studied later in this course all involved people and organizations as well as equipment: operators misreading an ambiguous indication, managers pressing ahead with a test under poor conditions, or an industry and regulator that did not act on new information about a hazard. Lesson 7 covers human reliability and lesson 12 covers safety culture. They are not soft topics at the end of the course; they are part of the same argument.
Nuclear security, which protects the plant against deliberate harm, and safeguards, which ensure nuclear material is used only for peaceful purposes, are related disciplines with their own requirements. This course concerns safety: protection against accidents and their consequences. Many design features serve both safety and security, and the three disciplines are coordinated at every plant.
Common mistakes
MistakeDefense in depth means having many barriers.
InsteadIt means independent layers of protection, both physical barriers and levels of prevention and mitigation; independence matters more than number.
MistakeRedundancy alone protects against common-cause failures.
InsteadIdentical redundant trains can fail together; diversity and separation are needed against shared causes.
MistakeSafety goals are limits that the plant must never exceed.
InsteadThey are targets for average risk that guide design and decisions, estimated with uncertainty by probabilistic assessment.
Summary and key terms
- The fundamental safety functions are to control reactivity, cool the fuel and confine radioactive material.
- Defense in depth combines physical barriers with five levels of prevention and mitigation.
- Redundancy, diversity, separation, the single-failure criterion and fail-safe design make the levels real.
- A shared cause that defeats several levels at once can dominate risk.
- Safety goals express how safe is safe enough in terms of core damage and release frequencies.
- Defense in depth
- Several independent layers of protection so that no single failure leads to harm.
- Redundancy
- Providing more trains or components than the minimum needed.
- Diversity
- Using different types of equipment or principles for the same function.
- Single-failure criterion
- The requirement that a safety function is performed despite any single active failure.
- Safety goal
- A quantitative or qualitative target for acceptable risk from a plant.
- Licensing basis
- The requirements, analyzes and commitments a plant must continue to meet.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Name the three fundamental safety functions.
Show answer
Control reactivity, cool the fuel and confine radioactive material.
Why can redundancy fail to protect against a flood?
Show answer
Identical trains in the same area can all be disabled by the same flood; separation and diversity are needed.
An event has frequency 1 × 10⁻³ per year and mitigation fails with probability 1 × 10⁻². What is the damage frequency?
Show answer
1 × 10⁻⁵ per year.
What is a fail-safe design?
Show answer
One in which failure leads to a safe state, such as rods dropping on loss of power.
Which level of defense covers off-site emergency response?
Show answer
Level 5.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.