
CISSP-110 · Lesson 5 of 12 · 26 min
Privacy law and transborder data flows in the US
Privacy law is one of the fastest-changing areas a security leader must track. Sub-domain 1.4 of the CISSP outline lists privacy issues, with examples such as the EU General Data Protection Regulation (GDPR), the California Consumer Privacy Act (CCPA), China's Personal Information Protection Law (PIPL) and South Africa's Protection of Personal Information Act (POPIA), together with transborder data flow. This lesson explains the principles that most privacy laws share, the main laws that apply in your country and internationally, breach notification duties, and how organizations manage transfers of personal information across borders.
Privacy principles
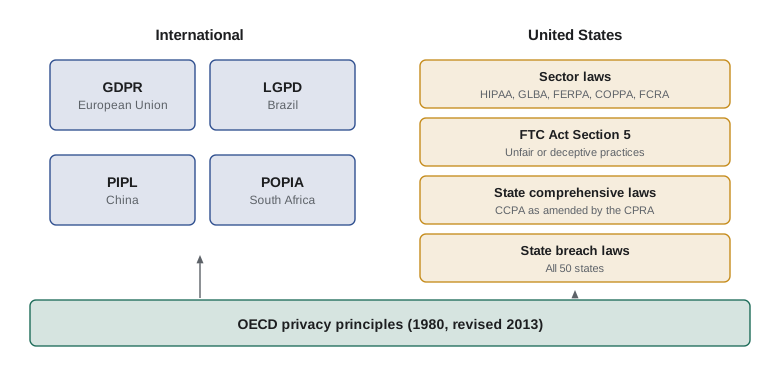
Most modern privacy laws trace back to the OECD Privacy Guidelines of 1980, revised in 2013. Their eight principles are collection limitation, data quality, purpose specification, use limitation, security safeguards, openness, individual participation and accountability. Canada's PIPEDA is built on ten fair information principles from the CSA Model Code: accountability, identifying purposes, consent, limiting collection, limiting use, disclosure and retention, accuracy, safeguards, openness, individual access, and challenging compliance. The GDPR expresses similar ideas as lawfulness, fairness and transparency; purpose limitation; data minimization; accuracy; storage limitation; integrity and confidentiality; and accountability.
For a security professional, two principles stand out. The safeguards principle requires security measures appropriate to the sensitivity of the information, which makes poor security a privacy violation in itself. The accountability principle requires an organization to remain responsible for personal information it transfers to service providers, which is why vendor contracts and assessments (Lesson 10) are privacy controls as well as security controls.
Privacy law uses some recurring terms. Personal information, or personal data, is information about an identifiable individual. Sensitive categories, such as health, financial, biometric and children's data, usually need stronger protection. The controller (or organization) decides why and how personal data is processed; the processor (or service provider) processes it on the controller's behalf. Pseudonymized data can still be linked back to a person with additional information and usually remains personal data; anonymized data cannot reasonably be linked back, although true anonymization is harder than it looks.
The main laws
In the United States, there is no single comprehensive federal privacy law. Instead, sector laws apply: HIPAA and the HITECH Act for health information held by covered entities and business associates; the Gramm-Leach-Bliley Act (GLBA) for financial institutions, including the FTC's Safeguards Rule, amended in 2023 to require a written information security program, a qualified individual to run it, encryption and multi-factor authentication, and notification to the FTC of incidents affecting 500 or more consumers within 30 days; FERPA for student records; COPPA for children under 13 online; and the Fair Credit Reporting Act. The FTC enforces against unfair or deceptive practices. States have filled the gap: the California Consumer Privacy Act, as amended by the CPRA and enforced by the California Privacy Protection Agency, gives residents rights to know, delete, correct and opt out of the sale or sharing of personal information, and by 2026 about twenty states had enacted comprehensive consumer privacy laws.
The GDPR applies to organizations established in the EU and to organizations elsewhere that offer goods or services to people in the EU or monitor their behavior. It requires a lawful basis for processing, such as consent, contract, legal obligation or legitimate interests; gives individuals rights of access, rectification, erasure, restriction, portability and objection; requires data protection impact assessments for high-risk processing; and requires many organizations to appoint a data protection officer. Fines can reach 20 million euros or 4 percent of worldwide annual turnover, whichever is higher. Many other countries, including Brazil (LGPD), China (PIPL) and South Africa (POPIA), have comprehensive laws with similar features.
Breach notification
Most privacy regimes now require organizations to notify regulators and affected individuals of certain breaches. The details matter: what counts as a breach, what harm threshold triggers notice, how fast notice must be given and what records must be kept. Security teams should build these rules into incident response plans in advance, because the clock usually starts when the organization becomes aware of the breach, not when the investigation ends.
In the United States, all fifty states, the District of Columbia and the territories have breach notification laws. They differ in the definition of personal information, the harm threshold, deadlines (commonly 'without unreasonable delay', with some states setting 30, 45 or 60 days) and whether the state attorney general must be told. Sector rules add more: HIPAA requires notice to individuals within 60 days of discovery and to the Department of Health and Human Services, with media notice for breaches affecting more than 500 residents of a state; the GLBA Safeguards Rule requires notice to the FTC within 30 days for 500 or more consumers; and public companies must disclose material cybersecurity incidents on Form 8-K Item 1.05 within four business days of determining materiality, under SEC rules in effect since December 2023 (industry groups have petitioned to narrow them, so check current status).
The GDPR requires controllers to notify the supervisory authority within 72 hours of becoming aware of a personal data breach unless it is unlikely to result in a risk to individuals, and to notify individuals without undue delay when the risk is high. Processors must notify the controller without undue delay. A single incident affecting customers in several countries can therefore trigger many different notification duties with different clocks.
Worked problem
Is the breach reportable?
An employee emails a spreadsheet of 1,200 customers' names, home addresses and dates of birth to the wrong external address. The recipient, a stranger, does not reply. Assess the notification question.
Show solution
- Was there unauthorized disclosure of personal information? Yes, to an outside party.
- Sensitivity: names, addresses and dates of birth together can support identity theft.
- Probability of misuse: unknown recipient, no confirmation of deletion, so misuse cannot be ruled out.
- Conclusion: the harm threshold (real risk of significant harm, or the state equivalent) is likely met; notify the regulator and individuals as required, attempt recall and confirmation of deletion, and record the incident.
Answer: Likely reportable. Document the assessment either way, because regulators may ask how the decision was made.
Transborder data flows
Personal data crosses borders constantly: cloud services, outsourced support, global human resources systems and analytics platforms all move it. Some laws restrict these transfers to protect individuals when their data leaves the country.
The GDPR permits transfers outside the European Economic Area only under specific mechanisms: an adequacy decision by the European Commission, appropriate safeguards such as standard contractual clauses or binding corporate rules, or narrow derogations. The Court of Justice of the EU invalidated the EU-US Privacy Shield in 2020 (the Schrems II decision), partly because of US surveillance law. The EU-US Data Privacy Framework, adopted in July 2023, restored a route for transfers to US organizations that self-certify, and the EU General Court upheld it in September 2025, although further appeals remain possible. Canada has held an adequacy decision for organizations subject to PIPEDA since 2001, reconfirmed in 2024.
In the United States, federal law generally does not restrict transferring personal data abroad, but new rules address national security concerns. The Protecting Americans' Data from Foreign Adversaries Act of 2024 restricts data brokers from transferring sensitive data of US individuals to designated foreign adversary countries, and a Department of Justice rule effective in 2025 restricts certain bulk transfers of sensitive personal data and government-related data to countries of concern, including China and Russia. Contracts with foreign customers often require US companies to accept GDPR-style transfer terms.
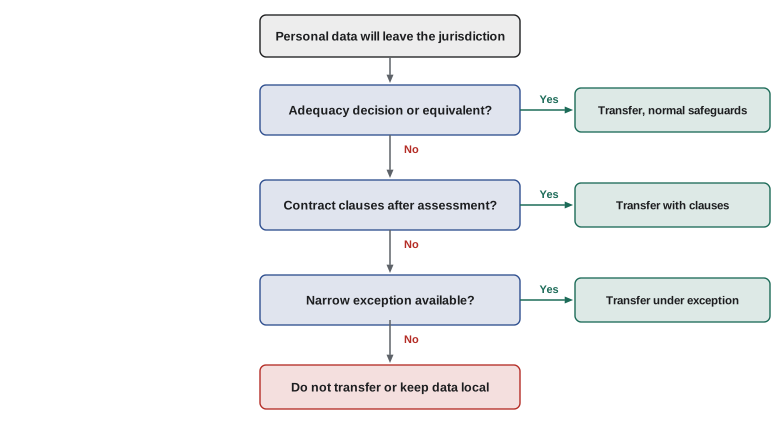
Data localization laws go further by requiring certain data to stay within a country. Russia, China and India have broad or sector-specific localization rules, and some public-sector and financial regulators impose them. Localization affects architecture choices such as which cloud regions to use and where backups are stored.
Privacy as a security leader's concern
Security and privacy teams work closely together. Security provides the safeguards; privacy defines what data may be collected, for what purposes and for how long. Privacy impact assessments (PIAs), or data protection impact assessments under the GDPR, are a joint tool: they map data flows, identify risks to individuals and recommend controls before a system goes live. Data minimization is also a security control, because data that was never collected, or was deleted on schedule, cannot be breached.
Worked problem
Estimating GDPR fine exposure
A company with worldwide annual turnover of 900 million euros suffers a serious breach caused by missing basic safeguards. What is the maximum fine tier for infringements of the GDPR's core principles?
Show solution
- The higher tier is the greater of 20 million euros or 4 percent of worldwide annual turnover.
- Four percent of turnover: \( 0.04 \times 900{,}000{,}000 = 36{,}000{,}000 \) euros.
- Compare: 36 million is greater than 20 million.
Answer: Up to 36 million euros. Actual fines depend on factors such as severity, cooperation and mitigation, and are usually far below the maximum.
Individual rights and privacy operations
Privacy laws give individuals rights that the organization must be able to honor quickly and securely. Common rights include access to the personal information held about them, correction of inaccurate information, deletion in certain cases, withdrawing consent, and objecting to some kinds of processing such as direct marketing or automated decision-making. Each right creates operational and security tasks: verifying the requester's identity so that information is not disclosed to an impostor, finding the person's data across systems and suppliers, responding within legal deadlines, and keeping records of requests.
Data mapping makes these tasks possible. An organization that knows where each category of personal information is collected, stored, processed and shared can answer access requests, plan breach responses, apply retention schedules and complete privacy impact assessments. Without a data map, a simple deletion request can take weeks of searching and still miss copies in backups, analytics platforms or supplier systems. Security teams contribute by maintaining asset inventories, classifying data and supporting secure deletion, so that privacy promises made to customers are actually kept.
Privacy obligations also extend to how long information is kept. Retention schedules should state how long each category of personal information is needed for its purpose or for legal reasons, and how it will be securely destroyed afterwards. Keeping data 'just in case' increases breach impact, complicates access requests and may itself breach the storage limitation principle.
Privacy is therefore both a legal duty and a design discipline that security leaders share.
Common mistakes
MistakeTreating privacy as only a legal team issue.
InsteadSafeguards and accountability principles make security central to privacy compliance.
MistakeAssuming pseudonymized data is no longer personal data.
InsteadIt can be re-linked and usually remains personal data.
MistakeStarting the notification clock after the investigation ends.
InsteadClocks usually start when the organization becomes aware of the breach.
MistakeBelieving outsourcing transfers accountability.
InsteadThe organization remains accountable for data held by its service providers.
MistakeForgetting that one incident can trigger several notification regimes.
InsteadMap notification duties by jurisdiction and sector in the incident plan.
Summary and key terms
- Most privacy laws share principles from the OECD Guidelines, including safeguards and accountability.
- Controllers decide purposes; processors act on their behalf; accountability stays with the controller.
- Domestic laws differ: the country column above lists the main laws and regulators that apply here.
- The GDPR applies extraterritorially, requires a lawful basis and allows fines up to 4 percent of turnover.
- Breach notification rules vary in harm thresholds and deadlines; the GDPR sets 72 hours to the regulator.
- Cross-border transfers need adequacy, contractual safeguards or exceptions; localization rules may require data to stay in country.
- Privacy impact assessments and data minimization link privacy and security.
- Personal information
- Information about an identifiable individual.
- Controller
- The organization that decides why and how personal data is processed.
- Processor
- An organization that processes personal data on a controller's behalf.
- Pseudonymization
- Replacing identifiers so data cannot be linked to a person without additional information.
- Anonymization
- Irreversibly removing the ability to identify individuals.
- Adequacy decision
- A finding that a country's law protects personal data to an equivalent standard.
- Standard contractual clauses
- Approved contract terms that permit GDPR transfers to countries without adequacy.
- Privacy impact assessment
- An assessment of privacy risks of a system or project before it goes live.
- Data localization
- A requirement that certain data be stored or processed within a country.
- Breach notification
- A legal duty to tell regulators or individuals about qualifying breaches.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Which 1980 guidelines underpin most privacy laws?
Show answer
The OECD Privacy Guidelines.
Who remains accountable when a processor mishandles data?
Show answer
The controller or organization that transferred it.
Within how many hours must a GDPR controller usually notify the regulator of a breach?
Show answer
72 hours.
What is the GDPR's maximum fine for core infringements?
Show answer
20 million euros or 4 percent of worldwide turnover, whichever is higher.
What replaced the EU-US Privacy Shield?
Show answer
The EU-US Data Privacy Framework (2023).
What are standard contractual clauses used for?
Show answer
To permit transfers of personal data to countries without an adequacy decision.
Why is data minimization a security control?
Show answer
Data that is not collected or kept cannot be breached.
Is pseudonymized data usually still personal data?
Show answer
Yes.
What does a privacy impact assessment examine?
Show answer
Data flows, risks to individuals and controls before a system goes live.
What is data localization?
Show answer
A legal requirement to keep certain data within a country.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.