
CISSP-113 · Lesson 11 of 12 · 30 min
Network monitoring, operations and regulation
A network that is well designed on paper can still be compromised if no one is watching it, if changes break its controls, or if the organization does not understand its legal obligations. This lesson covers the operational side of network security: collecting the right telemetry, monitoring and detection, network operations and change management, availability and capacity, and the legal and regulatory context in which networks are monitored and protected, including lawful interception, privacy, critical infrastructure rules and incident reporting. Security operations as a whole, including incident response and investigations, is the subject of CISSP-116; this lesson focuses on what is specific to networks.
Network telemetry
Monitoring begins with data, and different sources answer different questions. Full packet capture records every byte; it gives the most detail and is invaluable for investigations, but it is expensive to store, so it is usually kept for days rather than months and focused on key points. Flow records, such as NetFlow, IPFIX and sFlow from routers and switches or flow logs from cloud platforms, summarize each conversation: source and destination addresses, ports, protocol, bytes, packets and timestamps. They are compact enough to keep for months and reveal who talked to whom and how much. Logs from firewalls, proxies, VPN gateways, DNS resolvers, DHCP servers, wireless controllers and NAC systems record decisions and identities. Metadata from network detection tools adds protocol details such as TLS server names, HTTP hosts and certificate fingerprints even when content is encrypted.
Collection points matter. Network taps, passive devices that copy traffic from a link, are reliable and invisible to attackers; mirror or SPAN ports on switches are cheaper but can drop packets under load. Sensors at the internet edge see inbound and outbound traffic; sensors inside, between zones and in the data centre, see lateral movement that the edge never sees. In encrypted environments, the endpoint and the points where TLS terminates, such as reverse proxies and load balancers, become essential vantage points.
| Source | Answers | Retention (typical) | Limits |
|---|---|---|---|
| Full packet capture | Exactly what was sent | Days | Large storage; encrypted payloads unreadable |
| Flow records | Who talked to whom, when and how much | Months | No content |
| Firewall and proxy logs | What was allowed or blocked, and for whom | Months to years | Only what passes those devices |
| DNS logs | Which names hosts looked up | Months | Missed if hosts use outside resolvers |
| DHCP, NAC and VPN logs | Which device or user held which address | Months to years | Must be correlated by time |
| Endpoint telemetry | Which process made which connection | Weeks to months | Needs agents on every device |
Monitoring and detection
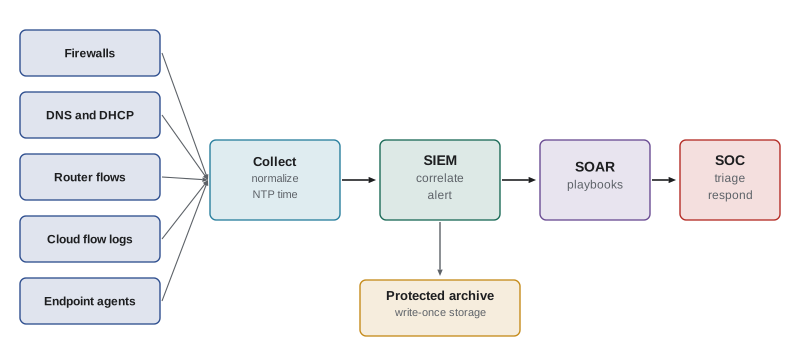
Logs are useful only if someone, or something, looks at them. A security information and event management system, SIEM, collects logs from many sources, normalizes them, correlates events across sources and raises alerts according to rules and analytics. Security orchestration, automation and response, SOAR, tools run playbooks that enrich alerts with context and automate steps such as blocking an address or isolating a host. Network detection and response, NDR, tools analyse traffic and flows with signatures, behavioural models and machine learning to spot anomalies such as scanning, beaconing and unusual data transfers. Extended detection and response, XDR, combines endpoint, network, identity and cloud signals.
Accurate time is the foundation of correlation. If devices' clocks drift, events cannot be placed in order and evidence may be challenged. All devices should synchronize to trusted, redundant time sources using NTP, ideally authenticated, and logs should record time zones explicitly or use UTC. Logs should be shipped promptly to a central store protected from tampering, with access controls and integrity protection such as write-once storage or hashing, because attackers routinely try to delete logs to cover their tracks.
Worked problem
Detecting beaconing in flow data
Flow records show a workstation connecting to the same external address every 300 seconds, plus or minus 5 seconds, around the clock, with small, nearly identical byte counts. Ordinary browsing is irregular. What does this suggest, and what should the analyst check?
Show solution
- Regular intervals with low variation and similar sizes are typical of automated check-ins: malware beaconing to command and control, or legitimate software checking for updates.
- Check the destination: domain age, reputation, TLS certificate details and whether other hosts contact it.
- Check the endpoint: which process opened the connections, when it was installed and whether it is approved software.
- If unexplained, contain the host under the incident response plan and search flows for other hosts with the same pattern.
Answer: The pattern suggests beaconing. Confirm with destination and endpoint context before acting, then contain and hunt for the same pattern elsewhere. Flow data found it without decrypting anything.
Detection content needs continuous improvement. Map detections to a framework such as MITRE ATT&CK to find gaps; test them with purple team exercises in which defenders and authorized testers work together; measure mean time to detect and respond; and tune rules to reduce false positives so that analysts focus on what matters. Threat intelligence about indicators, such as malicious domains and addresses, and about adversary behaviour should feed both blocking controls and detections.
Network operations and change management
Many security failures begin as operational changes: a temporary firewall rule never removed, a new cloud network created outside the approved design, a router replaced with default settings. Network change management requires that changes are requested, assessed for security and operational impact, approved, scheduled, implemented, tested and documented, with a rollback plan. Emergency changes need a fast path but must still be recorded and reviewed afterwards. Configuration management keeps approved baselines for each device type, compares running configurations against them and alerts on drift. Automation and infrastructure as code, discussed in lesson 9, make changes more consistent and auditable.
Network operations centres, NOCs, monitor availability and performance; security operations centres, SOCs, monitor threats. They must work together: a sudden traffic surge may be a DDoS attack or a successful product launch, and a failed link may be an accident or sabotage. Shared runbooks, communication channels and escalation paths prevent delays. Documentation, including current network diagrams, address plans, data flow maps and asset inventories, is a security control in its own right, because responders cannot defend or investigate what they cannot see.
Availability, capacity and resilience
Availability is part of security. Designs should remove single points of failure where the business requires it: redundant devices in high-availability pairs, diverse links from different carriers that do not share conduits, multiple DNS providers, geographically separate data centres or cloud regions, and dependable power. Capacity planning watches link utilization, device resources and growth trends so that normal peaks, as well as attacks, do not exhaust resources. Quality of service policies prioritize critical traffic such as voice, control systems and management under congestion. Resilience must be tested: failover that has never been exercised often fails when needed.
Worked problem
Availability of redundant links
A branch has one internet link with 99.5 % availability. Adding a second link from a different carrier, also 99.5 % available and failing independently, gives what combined availability, and how much expected downtime per year does it remove?
Show solution
- One link: unavailable 0.5 % of the time, about 0.005 × 8,760 h ≈ 43.8 hours a year.
- Both down at once (independent failures): 0.005 × 0.005 = 0.000025.
- Combined availability: 1 − 0.000025 = 99.9975 %.
- Expected downtime: 0.000025 × 8,760 ≈ 0.22 hours, about 13 minutes a year.
Answer: About 99.9975 %, cutting expected downtime from about 44 hours to about 13 minutes a year, provided the links truly fail independently. Shared conduits, a shared upstream or a single router undo much of the benefit.
Legal and regulatory context
Monitoring networks touches people's communications, so it is governed by law. Organizations generally may monitor their own networks to protect them, but they should have clear policies, tell users that monitoring takes place, collect only what they need, restrict access to monitoring data and keep it no longer than necessary. Interception of communications in transit, especially those of third parties, and access to stored communications are regulated by criminal and privacy laws that differ between countries. Legal counsel should review monitoring programs, TLS inspection and retention policies, and investigations that may lead to court should follow evidence-handling procedures.
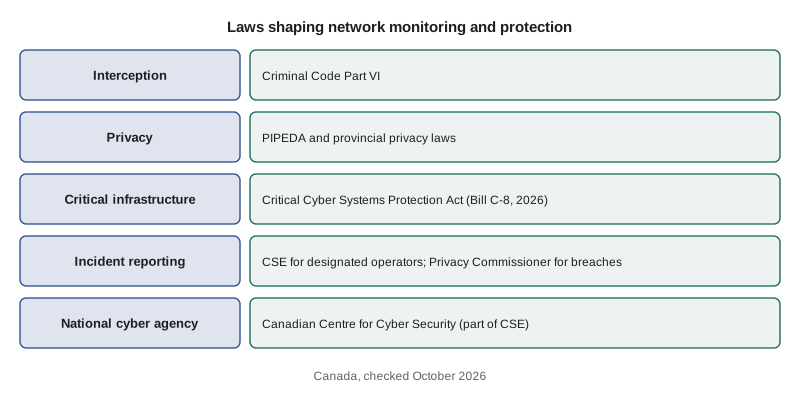
In Canada, Part VI of the Criminal Code makes it an offence to intercept private communications, with exceptions that include interception by a person providing a communications service when necessary to provide the service or protect it, and interception with the consent of one party. Federal privacy law, PIPEDA, governs personal information collected by private-sector organizations in commercial activity, including employee monitoring in federally regulated workplaces, and provincial laws such as those of Quebec, British Columbia and Alberta apply in their own spheres. Employers should be able to show that monitoring is reasonable, proportionate and disclosed. Lawful access by police generally requires judicial authorization. A bill on lawful access, Bill C-22, the Lawful Access Act, 2026, introduced in March 2026 and including a proposed Supporting Authorized Access to Information Act requiring some service providers to maintain interception capabilities, was before a House of Commons committee at the time of writing (checked October 2026).
Critical infrastructure and incident reporting
Governments increasingly impose cyber security duties on operators of critical infrastructure, including requirements to have security programs, manage supply chain risks and report significant incidents within short deadlines. Security managers must know which regimes apply to their organization, because reporting obligations can start the clock as soon as an incident is suspected, and a missed deadline can bring penalties in addition to the harm of the incident itself.
In Canada, Bill C-8, which received royal assent on 16 June 2026, amends the Telecommunications Act to make security an explicit policy objective and to let the government order telecommunications providers to take security measures, effective on royal assent, and enacts the Critical Cyber Systems Protection Act. That act will require designated operators of vital services in federally regulated sectors, finance, telecommunications, energy and transportation, to establish cyber security programs, mitigate supply chain and third-party risks, report cyber security incidents to the Communications Security Establishment within deadlines set by regulation and comply with directions, with significant penalties for non-compliance. It is being implemented in phases through regulations (checked October 2026). Separately, privacy breaches involving a real risk of significant harm must be reported to the Privacy Commissioner of Canada under PIPEDA, and to provincial commissioners where provincial law applies. The Canadian Centre for Cyber Security publishes guidance, including its baseline controls for small and medium organizations, and Government of Canada systems follow the ITSG-33 risk management guidance.
Worked problem
An incident reporting clock
On Monday at 09:00 a SOC analyst confirms that an attacker accessed a payment processor's network and may have taken customer data. Leadership determines on Wednesday at 15:00 that the incident is material. List the immediate reporting considerations a security manager should raise.
Show solution
- Activate the incident response plan and legal counsel immediately; preserve evidence, including network logs and packet captures.
- Identify every regime that applies: critical infrastructure reporting to the national cyber agency, privacy breach notification to regulators and affected individuals, securities disclosure if the company is public, sector regulators and contractual notices to banks and card brands.
- Note each regime's trigger and deadline; some start when an incident is reasonably believed to have occurred, others when materiality is determined or when harm is assessed.
- Assign owners for each notification, track deadlines and keep a record of decisions and their timing.
Answer: Several clocks may be running at once with different triggers. Counsel-led, documented tracking of each obligation from the first hours of the incident avoids missed deadlines.
Thinking like a manager
In operations, the manager's job is to make sure the right telemetry exists, that someone acts on it, that changes do not silently undo controls and that availability is designed and tested. In law and regulation, the job is to know which obligations apply, to make monitoring lawful, proportionate and disclosed, and to have reporting processes ready before an incident. Exam questions often reward the answer that involves legal counsel, documented policy and preparation over the purely technical response.
Common mistakes
MistakeCollecting logs but never reviewing or correlating them.
InsteadFeed logs to a SIEM with tuned detections and staffed or automated response.
MistakeLetting device clocks drift.
InsteadSynchronize all devices to redundant, trusted time sources and record time zones or use UTC.
MistakeStarting TLS inspection or employee monitoring without legal review.
InsteadInvolve counsel, publish policies, notify users and minimize what is collected.
MistakeAssuming two links from different carriers are automatically independent.
InsteadVerify physical path diversity and remove shared failure points.
MistakeWorking out incident reporting duties during an incident.
InsteadMap applicable reporting regimes, triggers and deadlines in advance and rehearse them.
Summary and key terms
- Packet capture, flow records, device logs and endpoint telemetry answer different investigative questions.
- SIEM, SOAR, NDR and XDR collect, correlate, automate and detect across sources; accurate time is essential.
- Change and configuration management prevent operational changes from undermining security.
- Redundancy, capacity planning, quality of service and tested failover protect availability.
- Network monitoring must comply with interception and privacy laws; involve legal counsel.
- Critical infrastructure laws, such as Canada's Critical Cyber Systems Protection Act and the US CIRCIA, impose programs and incident reporting.
- Prepare reporting processes in advance, because several deadlines may run at once.
- Flow record
- A summary of a network conversation: addresses, ports, protocol, bytes and times.
- Network tap
- A passive device that copies traffic from a link for monitoring.
- SIEM
- Security information and event management, which collects and correlates logs.
- SOAR
- Security orchestration, automation and response, which runs playbooks on alerts.
- NDR
- Network detection and response, which analyses traffic for threats.
- Beaconing
- Regular automated check-ins from a compromised host to command and control.
- Configuration drift
- Divergence of a device's running configuration from its approved baseline.
- Lawful interception
- Interception of communications under legal authority, supported by providers.
- CIRCIA
- The US Cyber Incident Reporting for Critical Infrastructure Act of 2022.
- Critical Cyber Systems Protection Act
- The Canadian law enacted by Bill C-8 imposing cyber duties on designated operators.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Which telemetry source is compact enough to keep for months and shows who talked to whom?
Show answer
Flow records.
Why are taps preferred to SPAN ports for critical monitoring?
Show answer
They are passive and reliable, while SPAN ports can drop packets under load.
What does a SOAR tool do?
Show answer
Runs playbooks that enrich alerts and automate response steps.
Why is NTP important to security monitoring?
Show answer
Accurate time lets events from different sources be correlated and supports evidence.
What pattern in flow data suggests beaconing?
Show answer
Regular connections at fixed intervals with similar sizes to the same destination.
What should every emergency network change receive afterwards?
Show answer
Documentation and a post-implementation review.
Two independent links are each 99 % available. What is their combined availability?
Show answer
99.99 %.
Who should review TLS inspection and monitoring policies?
Show answer
Legal counsel, along with privacy and HR stakeholders.
Within what time must covered entities report covered incidents under CIRCIA once the rule takes effect?
Show answer
72 hours, and ransom payments within 24 hours.
Which Canadian agency receives incident reports under the Critical Cyber Systems Protection Act?
Show answer
The Communications Security Establishment.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.