
CISSP-160 · Lesson 7 of 12 · 40 min
Practicing Domains 5 and 6: identity and access management, and assessment and testing
Domains 5 and 6 together carry about 25 % of the 2024 outline and almost exactly the same share of the 2027 outline, with Domain 5 rising slightly. They fit naturally together. Domain 5 is about deciding who can do what and making that decision stick; Domain 6 is about checking that controls, including access controls, actually work. Many items combine them, for example by asking how an organization should review access rights or test whether its authentication works as intended.
Tomás's diagnostic showed Domain 5 slightly below target and Domain 6 well below. Like many engineers, he knows how to configure an identity provider but is less sure of the vocabulary of assurance: audits versus assessments, the types of testing, what a SOC report covers and who should receive findings. Hannah is the opposite. This lesson works through both domains with ten original practice items.
Domain 5 at a glance
| Area | Ideas that appear often | Course that taught it |
|---|---|---|
| Identification and authentication | Factors (knowledge, possession, inherence), multifactor authentication, passwordless and passkeys, biometrics and their error rates | CISSP-114 lessons 2 to 4 |
| Federation and single sign-on | SAML, OAuth 2.0 (authorization), OpenID Connect (authentication), trust between identity and service providers | CISSP-114 lesson 5 |
| Authorization models | Discretionary, mandatory, role-based, rule-based, attribute-based and risk-adaptive access control | CISSP-114 lesson 6 |
| Identity life cycle | Provisioning, review, recertification, privilege creep, deprovisioning, joiner-mover-leaver | CISSP-114 lessons 7 to 8 |
| Privileged access | Privileged access management, just-in-time access, break-glass accounts, separation of duties | CISSP-114 lesson 9 |
| Physical and logical access | Badges, mantraps, visitor control, the link between physical and logical identity | CISSP-114 lessons 10 to 11 |
Biometric items often test two error rates. The false rejection rate (type I error) is the share of legitimate users wrongly rejected; the false acceptance rate (type II error) is the share of impostors wrongly accepted. Tightening sensitivity lowers false acceptance and raises false rejection. The crossover error rate, where the two are equal, is used to compare systems: the lower it is, the more accurate the system.
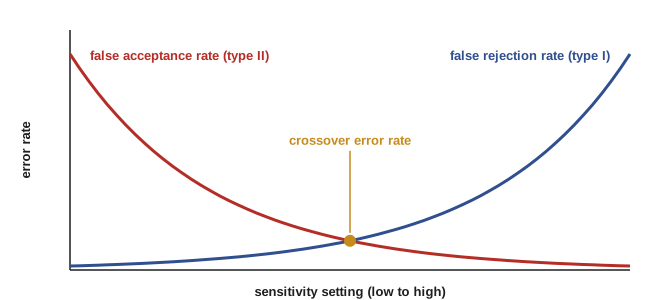
The 2027 outline names some newer ideas explicitly. Passwordless authentication, including passkeys built on the FIDO2 and WebAuthn standards, replaces shared secrets with public-key credentials bound to a device and a site, which resists phishing. Risk-adaptive access control adjusts decisions using signals such as device health, location and behavior. Both were covered in CISSP-114, and both are likely to appear more often in later exams.
Domain 6 at a glance
| Area | Ideas that appear often | Course that taught it |
|---|---|---|
| Assessment strategy | Internal, external and third-party assessments, audit independence, scoping and rules of engagement | CISSP-115 lessons 1 to 2 |
| Testing types | Vulnerability assessment, penetration testing (as an authorized, managed engagement), code review, fuzzing, misuse cases, test coverage | CISSP-115 lessons 3 to 7 |
| Security control testing | Log reviews, synthetic transactions, real user monitoring, breach and attack simulation (concept), account management reviews | CISSP-115 lessons 6 and 8 |
| Metrics and reporting | Key performance and risk indicators, reporting to management, exception handling | CISSP-115 lessons 9 to 10 |
| Audit reports | SOC 1, SOC 2 and SOC 3; Type 1 and Type 2; ISO/IEC 27001 certification audits | CISSP-115 lesson 11 |
Testing items reward precise terms. A vulnerability assessment finds and ranks weaknesses; a penetration test, carried out under written authorization and agreed rules of engagement, tests whether weaknesses can actually be used to reach a goal. Static testing examines code without running it; dynamic testing examines running software. A SOC 2 Type 1 report describes control design at a point in time; a Type 2 report also tests operating effectiveness over a period, usually six to twelve months.
Practice items: Domain 5
Worked problem
Item 1: counting factors
A user logs in with a password and then answers a security question about their first pet. How many authentication factors are used? (A) One. (B) Two. (C) Three. (D) It depends on the strength of the password.
Show solution
- Classify each method by factor type: a password is something you know; a security question is also something you know.
- Two methods of the same type count as one factor.
Answer: A. Both are knowledge factors, so this is single-factor authentication, however many steps it has.
Worked problem
Item 2: protocols in federation
Ridgeline wants partners to sign in to its merchant portal with their own corporate accounts, and the portal needs to know who the user is. Which protocol is designed for this authentication purpose on top of OAuth 2.0? (A) OAuth 2.0 alone. (B) OpenID Connect. (C) RADIUS. (D) LDAP.
Show solution
- Stem: authentication (who the user is) using a partner's identity provider, built on OAuth 2.0.
- OAuth 2.0 is an authorization framework; on its own it delegates access, not identity.
- RADIUS and LDAP are not federation protocols for web sign-in across organizations.
- OpenID Connect adds an identity layer on OAuth 2.0.
Answer: B. OpenID Connect provides federated authentication on top of OAuth 2.0.
Worked problem
Item 3: privilege creep
An employee who has moved through four roles at Ridgeline over six years still has access from every previous role. Which process would BEST have prevented this? (A) Stronger password rules. (B) Periodic access reviews and removal of access when people change roles. (C) Mandatory vacations. (D) Encryption of the employee's laptop.
Show solution
- Identify the problem: privilege creep, the build-up of access over time.
- Passwords, vacations and encryption do not remove unneeded access.
- The mover step of the identity life cycle should remove old access, and periodic recertification catches what was missed.
Answer: B. Access reviews and timely removal of access on role changes prevent privilege creep.
Worked problem
Item 4: choosing an access model
Ridgeline wants access to payment data to depend on the user's department, the data's classification, the time of day and whether the device is managed. Which access control model BEST supports this? (A) Discretionary access control. (B) Mandatory access control. (C) Role-based access control. (D) Attribute-based access control.
Show solution
- Stem: decisions based on several attributes of user, resource and environment.
- DAC lets owners grant access at their discretion; MAC uses fixed labels and clearances; RBAC grants access by role.
- ABAC evaluates policies over attributes such as department, classification, time and device state.
Answer: D. Attribute-based access control evaluates multiple attributes against policy.
Worked problem
Item 5: emergency access
Ridgeline's production database can be administered only through a privileged access management system. What is the BEST way to provide access if that system fails during an outage? (A) Give all administrators a permanent local admin account. (B) Maintain a sealed break-glass account with strong controls, monitoring and mandatory review after use. (C) Disable authentication during outages. (D) Share the root password in a team chat channel.
Show solution
- Stem: BEST emergency access when the normal path fails.
- A creates standing privilege; C and D are unacceptable.
- B provides controlled, auditable emergency access that is used rarely and reviewed every time.
Answer: B. A tightly controlled break-glass account, monitored and reviewed after every use.
Practice items: Domain 6
Worked problem
Item 6: which report to request
Ridgeline wants assurance that a cloud provider's security controls operated effectively over the past year. Which report should it request? (A) SOC 1 Type 1. (B) SOC 2 Type 1. (C) SOC 2 Type 2. (D) SOC 3.
Show solution
- Stem: security controls, operating effectiveness, over a period.
- SOC 1 covers controls relevant to financial reporting. Type 1 reports describe design at a point in time. SOC 3 is a short general-use summary without detailed testing results.
- SOC 2 Type 2 covers security and related trust services criteria and tests operating effectiveness over a period.
Answer: C. A SOC 2 Type 2 report tests operating effectiveness over the review period.
Worked problem
Item 7: before a penetration test
Ridgeline is hiring a firm to perform a penetration test of its payment API. What must be in place BEFORE testing begins? (A) A press release announcing the test. (B) Written authorization from an appropriate executive and agreed rules of engagement and scope. (C) Disabling all monitoring so the testers are not detected. (D) A guarantee from the testers that they will find vulnerabilities.
Show solution
- Stem: what must exist before testing.
- Testing without written authorization may be unlawful and can disrupt operations.
- Rules of engagement set scope, timing, methods, contacts and how to stop the test if something goes wrong.
- A, C and D are unnecessary or harmful.
Answer: B. Written authorization and agreed rules of engagement and scope come first.
Worked problem
Item 8: testing a feature that is not yet live
Developers want to find security flaws in source code early, before the application can even be run. Which approach fits BEST? (A) Dynamic application security testing. (B) Static application security testing or manual code review. (C) Real user monitoring. (D) A penetration test of production.
Show solution
- Stem: find flaws before the code can run.
- Dynamic testing, real user monitoring and production penetration tests all need running software.
- Static analysis and code review examine source code directly.
Answer: B. Static analysis and code review work on code that is not yet running.
Worked problem
Item 9: monitoring availability
Ridgeline wants to know immediately if its checkout page stops working at 3 a.m., when few customers are online. Which technique BEST provides this? (A) Real user monitoring. (B) Synthetic transactions that run scripted checkouts at regular intervals. (C) Annual penetration testing. (D) Reviewing logs once a week.
Show solution
- Stem: detect failure when real traffic is light.
- Real user monitoring needs real users. Annual tests and weekly reviews are too infrequent.
- Synthetic transactions run scripted checks continuously, whether or not customers are active.
Answer: B. Synthetic transactions test functions on a schedule regardless of real traffic.
Worked problem
Item 10: reporting audit findings
An internal auditor finds that terminated employees kept access to a reporting system for weeks. To whom should the auditor report the finding? (A) Only the IT administrator who manages the system. (B) Management responsible for the process, through the audit reporting line to those charged with governance. (C) The terminated employees. (D) A regulator, before telling management.
Show solution
- Stem: who receives an audit finding.
- Audit independence means reporting through the audit function to management and, ultimately, to the audit committee or board, not only to the person who runs the system.
- Going to a regulator first bypasses management's chance to respond and is not normal practice for an internal auditor.
Answer: B. Findings go to responsible management through the audit reporting line, which preserves independence.
A quick check on biometric rates
The program below calculates the error rates from test results for two biometric readers that Ridgeline is evaluating for its data center doors, and identifies the one with the lower average error. A real evaluation would compare crossover error rates across many sensitivity settings; this is a simplified version for practice.
# Compare two biometric readers using false rejection and false acceptance rates
readers = {
    "Reader A": {"genuine_attempts": 2000, "false_rejects": 46, "impostor_attempts": 2000, "false_accepts": 12},
    "Reader B": {"genuine_attempts": 2000, "false_rejects": 20, "impostor_attempts": 2000, "false_accepts": 28},
}
for name, r in readers.items():
    frr = r["false_rejects"] / r["genuine_attempts"]
    far = r["false_accepts"] / r["impostor_attempts"]
print(f"{name}: FRR (type I) {frr:.1%} FAR (type II) {far:.1%} average {(frr + far) / 2:.2%}")Reader A: FRR (type I) 2.3% FAR (type II) 0.6% average 1.45% Reader B: FRR (type I) 1.0% FAR (type II) 1.4% average 1.20%
Reader A rejects more genuine users but accepts fewer impostors; Reader B is the reverse. For a data center door, where admitting an impostor is the more serious failure, Ridgeline might prefer Reader A even though its average error is higher. The exam may ask exactly this kind of judgment: which error matters more depends on what is being protected.
Patterns to remember
| If the item asks... | The answer is usually... |
|---|---|
| How many factors two knowledge methods provide | One |
| Which protocol adds authentication to OAuth 2.0 | OpenID Connect |
| How to stop privilege creep | Access reviews and removal of access on role changes |
| Which model uses many attributes and conditions | Attribute-based access control |
| Which report shows controls operated over a period | SOC 2 Type 2 (security) or SOC 1 Type 2 (financial reporting) |
| What must exist before a penetration test | Written authorization and rules of engagement |
| How to test code that cannot yet run | Static analysis or code review |
| How to monitor a function when traffic is low | Synthetic transactions |
Common mistakes
MistakeCounting two knowledge methods as two factors.
InsteadFactors are types: knowledge, possession and inherence. Two of the same type count once.
MistakeCalling OAuth 2.0 an authentication protocol.
InsteadOAuth 2.0 is for authorization; OpenID Connect adds authentication.
MistakeRequesting a Type 1 report when effectiveness over time is needed.
InsteadType 2 reports test operating effectiveness over a period.
MistakeStarting a penetration test on verbal approval.
InsteadObtain written authorization and agree scope and rules of engagement first.
MistakeAssuming the lowest average error is always the best biometric choice.
InsteadConsider which error is worse for the asset; the crossover error rate is the standard comparison.
Summary and key terms
- Domains 5 and 6 together carry about a quarter of the exam and often combine in items about reviewing and testing access.
- Authentication factors are types; passkeys and FIDO2 provide phishing-resistant passwordless authentication.
- OAuth 2.0 authorizes, OpenID Connect authenticates and SAML exchanges assertions between identity and service providers.
- Access models differ in who decides and on what basis: DAC, MAC, RBAC, rule-based, ABAC and risk-adaptive.
- Assessment items turn on precise terms: vulnerability assessment versus penetration test, static versus dynamic, Type 1 versus Type 2.
- Penetration tests need written authorization and rules of engagement; audit findings go to management through the audit reporting line.
- False rejection rate (FRR)
- The share of legitimate users a biometric system wrongly rejects; a type I error.
- False acceptance rate (FAR)
- The share of impostors a biometric system wrongly accepts; a type II error.
- Crossover error rate (CER)
- The point at which FRR and FAR are equal, used to compare biometric systems.
- Privilege creep
- The gradual build-up of access rights beyond what a user's current role needs.
- Synthetic transaction
- A scripted transaction run on a schedule to test that a system works.
- SOC 2 Type 2
- An audit report on controls relevant to security and related criteria that tests their operating effectiveness over a period.
Practice problems
Work each problem on paper first, then reveal the answer to check.
A user signs in with a smart card and a PIN. How many factors are used?
Show answer
Two: possession (card) and knowledge (PIN).
What does a lower crossover error rate indicate?
Show answer
A more accurate biometric system.
Which access model lets data owners grant access at their discretion?
Show answer
Discretionary access control.
What is the difference between a SOC 2 Type 1 and Type 2 report?
Show answer
Type 1 covers design at a point in time; Type 2 also tests operating effectiveness over a period.
Which testing approach examines source code without running it?
Show answer
Static application security testing or code review.
Reader X has FRR 3 % and FAR 0.5 %; Reader Y has FRR 1 % and FAR 2 %. Which suits a high-security vault better?
Show answer
Reader X, because its false acceptance rate is lower.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.