
CISSP-117 · Lesson 11 of 12 · 25 min
Acquiring software securely and AI-assisted development
Most of the software an organization runs was not written by its own developers. It buys commercial products, subscribes to software as a service, adopts open source applications, hires contractors to build custom systems, lets business users assemble applications on low-code platforms and, increasingly, has developers write code with the help of AI assistants. The CISSP objective 'assess the security impact of acquired software' asks managers to evaluate and control the risks that come with each of these routes. This lesson covers the acquisition routes, the due diligence and contract terms that manage their risks, and the specific questions raised by AI in development.
Acquisition routes and their risks
| Route | What the organization controls | Main security concerns |
|---|---|---|
| Commercial off-the-shelf (COTS) | Configuration, deployment, patching | Vendor development practices, vulnerabilities, patch timeliness, end of support |
| Software as a service (SaaS) | Configuration, identities, data put into it | Provider security, data location, shared responsibility, exit and data return |
| Open source applications | Everything, if it has the skills | Maintenance, community health, support, license obligations |
| Custom development by a contractor | Requirements, acceptance, contract terms | Contractor practices, code ownership, hidden functionality, knowledge transfer |
| Low-code and citizen development | Platform settings and governance | Unreviewed applications, data sprawl, excessive permissions, shadow IT |
| Managed services and outsourcing | Contract and oversight | Access to the organization's systems, subcontractors, incident cooperation |
The common thread is that buying software transfers some work to others but never transfers accountability. If a SaaS provider leaks customer data, the organization that collected the data still answers to regulators and customers. Due diligence before purchase and oversight afterwards are therefore part of due care.
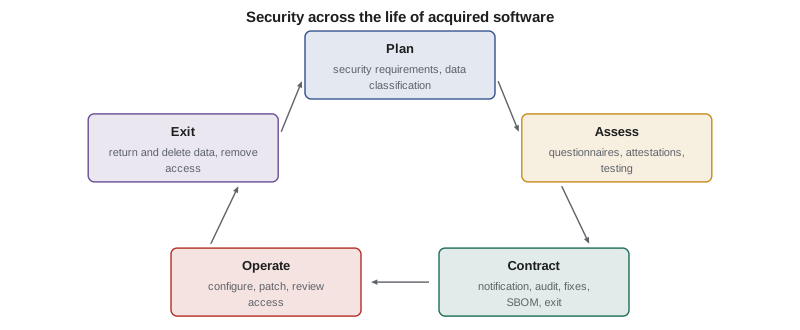
Due diligence before acquisition
Security assessment should begin when requirements are written, not after a product has been chosen. The requirements for an acquisition should include security requirements derived from the data the software will handle and the risks of the business process, such as support for the organization's single sign-on and multifactor authentication, role-based access, audit logging that can be exported to the SIEM, encryption, data residency, and timely security patches. Products that cannot meet mandatory requirements should be eliminated early, before the business becomes attached to them.
Supplier assessment draws on several kinds of evidence. Security questionnaires, ideally based on standards such as the Cloud Security Alliance's CAIQ or the Shared Assessments SIG, collect the supplier's own statements. Independent attestations carry more weight: a SOC 2 Type II report describes the operating effectiveness of a service organization's controls over a period, usually twelve months, as tested by an independent auditor; ISO/IEC 27001 certification shows that an information security management system meets the standard. Reports must be read, not just collected: check the scope, the period, exceptions found by the auditor and the complementary user entity controls the customer must perform. For software products, ask about the supplier's secure development practices, such as alignment with the NIST SSDF, SBOM availability, vulnerability disclosure policy, average time to fix critical vulnerabilities and support lifetime. Where the risk justifies it, the organization can test the product itself or commission a third-party assessment, within the limits the license allows.
Public sector buyers add their own frameworks. US federal agencies use cloud services authorized under FedRAMP, whose requirements have been modernized through the FedRAMP 20x initiative since 2025, and defense contractors must meet the Cybersecurity Maturity Model Certification (CMMC) program. Many states rely on similar programs, such as GovRAMP (formerly StateRAMP). Private sector buyers in regulated industries, such as banks under the 2023 interagency guidance on third-party relationships, must perform risk-based due diligence and keep oversight of third-party arrangements throughout their life.
# Weighted supplier security assessment for a SaaS candidate (illustrative weights and scores 0-5)
criteria = {
    'SSO and MFA support':            (0.15, 5),
    'Independent attestation (SOC 2 Type II, ISO 27001)': (0.20, 4),
    'Secure development evidence (SSDF, SBOM)': (0.15, 2),
    'Vulnerability disclosure and patch times': (0.15, 3),
    'Logging and SIEM export':        (0.10, 4),
    'Data residency and encryption':  (0.15, 5),
    'Exit: data return and deletion': (0.10, 2),
}
mandatory = {'SSO and MFA support': 3, 'Data residency and encryption': 4}
score = sum(w * s for w, s in criteria.values())
fails = [k for k, minimum in mandatory.items() if criteria[k][1] < minimum]
print(f'Weighted score: {score:.2f} / 5')
print('Mandatory criteria met' if not fails else 'Mandatory failures: ' + ', '.join(fails))
weak = [k for k, (w, s) in criteria.items() if s <= 2]
print('Address in contract or compensate:', '; '.join(weak))Weighted score: 3.65 / 5 Mandatory criteria met Address in contract or compensate: Secure development evidence (SSDF, SBOM); Exit: data return and deletion
Contract terms
The contract is where security expectations become enforceable. Security schedules or addenda commonly cover: compliance with stated security standards; notification of security incidents within a defined time; the right to audit or to receive independent audit reports annually; vulnerability management commitments, including maximum times to fix critical vulnerabilities and notification of vulnerabilities affecting the customer; provision of SBOMs on request; data location, encryption, return and deletion at the end of the contract; restrictions on subcontractors; background checks for personnel with access; cooperation in investigations; and the supplier's support lifetime for each version. For custom development, contracts should also state who owns the source code, require delivery of source and build instructions, prohibit undisclosed functionality such as backdoors and time bombs, require the contractor to follow the organization's secure coding standard, and define security acceptance testing before payment.
Software escrow addresses the risk that a supplier goes out of business or stops supporting a critical product. The supplier deposits source code, build instructions and documentation with a neutral escrow agent, to be released to the customer if defined events occur. Escrow is only useful if the deposit is kept current and verified, and if the customer has or can obtain the skills to maintain the code.
Operating acquired software
After purchase, the organization must keep doing its part. That includes secure configuration (default settings in commercial products and SaaS tenants are often permissive), applying vendor patches promptly, monitoring the supplier's security notices, reviewing SaaS configuration regularly with tools such as SaaS security posture management, reviewing user access, integrating logs, and reassessing the supplier periodically and after significant incidents. CISSP-112 and CISSP-116 cover configuration and patch management. Under the shared responsibility model, a SaaS provider secures its platform, but the customer remains responsible for who can access its tenant, how the tenant is configured and what data is placed there.
Low-code platforms and citizen developers
Low-code and no-code platforms let business users build applications, automations and integrations with little or no traditional programming. They deliver real value, but they also create applications that no developer has reviewed, connect to sensitive data with the creator's own permissions, and multiply quickly beyond the knowledge of IT. Governance should include an inventory of citizen-built applications, environment separation between personal experiments and business-critical solutions, data loss prevention policies that restrict which connectors can be combined, least-privilege service connections rather than personal credentials, a review path for applications that become important, and training for citizen developers. OWASP has published a Top 10 for low-code and no-code risks that is a useful checklist.
AI-assisted development
AI coding assistants based on large language models suggest code, explain unfamiliar code, write tests and can carry out multi-step development tasks as agents. Surveys show most developers now use them. They can raise productivity, and they can also introduce new risks that a manager must govern.
| Risk | Description | Controls |
|---|---|---|
| Insecure suggestions | Generated code can contain the same weaknesses found in the public code it learned from, presented confidently | Same review, testing and scanning as human code; secure coding standard applies; security-focused prompts and rules |
| Hallucinated dependencies | Assistants sometimes suggest packages that do not exist, which attackers can register | Approved package lists, internal proxy, review of every new dependency |
| Data leakage | Source code, secrets or customer data sent to an external service | Enterprise agreements with no training on customer data, approved tools only, secrets kept out of code, data classification rules |
| License and provenance | Suggestions resembling licensed code | Tools with duplicate-detection filters, legal guidance, SCA |
| Over-privileged agents | Agents that can run commands, change repositories or reach production | Least privilege, sandboxed environments, human approval for consequential actions, logging |
| Skill erosion and overreliance | Developers accepting code they do not understand | Training, review accountability: the human who merges the code owns it |
The guiding principle is that AI-generated code is code like any other and enters the product only through the same controls: review by an accountable human, automated scanning, tests and the security gate. The organization should publish an acceptable use policy that names approved tools, states what data may be shared with them, and requires that the developer who merges code is responsible for it regardless of its source.
Organizations that build AI features into their own products face further risks. The OWASP Top 10 for Large Language Model Applications (2025 edition) lists risks such as prompt injection, sensitive information disclosure, supply chain risks in models and datasets, excessive agency and improper output handling. Models and datasets are now part of the software supply chain: they should be obtained from trusted sources, inventoried (some organizations extend their SBOMs into AI bills of materials), scanned where possible and documented with model cards. NIST SP 800-218A, finalized in 2024, extends the SSDF with practices for developing generative AI and dual-use foundation models. AI-430 and AI-460 cover AI safety, evaluation and responsible AI in depth.
Worked problem
Approving an AI coding assistant at Ridgeline
Ridgeline's developers ask to use an AI coding assistant. Some already use free consumer versions with company code. The CTO asks security for a recommendation.
Show solution
- Stop the immediate leak: tell developers that consumer tools may not be used with company code and explain why.
- Select an enterprise offering whose contract prohibits training on Ridgeline's code and data, supports single sign-on and provides usage logs; complete a supplier assessment.
- Publish an acceptable use policy: approved tool only, no secrets or customer data in prompts, all generated code goes through normal review, scanning and testing, and the developer who merges it owns it.
- Strengthen supporting controls: new-dependency review to catch hallucinated packages, secrets scanning already in place, and a three-month review of defect and vulnerability trends in AI-assisted code.
Answer: Approve an enterprise tool under contract, govern its use with a clear policy, and rely on the existing development controls rather than trusting generated code.
Common mistakes
MistakeAssessing security only after a product has been chosen.
InsteadInclude security requirements in the acquisition from the start and eliminate products that fail mandatory criteria.
MistakeFiling SOC 2 reports without reading them.
InsteadCheck scope, period, exceptions and the complementary controls the customer must perform.
MistakeAssuming the SaaS provider is responsible for the tenant configuration.
InsteadApply the shared responsibility model: the customer secures access, configuration and data.
MistakePaying a contractor before security acceptance testing.
InsteadDefine security acceptance criteria, code ownership and source delivery in the contract.
MistakeLetting citizen-built applications grow without oversight.
InsteadInventory them, separate environments, restrict connectors and review critical apps.
MistakeTrusting AI-generated code because the tool is reputable.
InsteadTreat it like any other code: human review, scanning, testing and accountable ownership.
Summary and key terms
- Acquisition routes include COTS, SaaS, open source applications, contracted development, low-code platforms and managed services; accountability is never transferred.
- Due diligence uses security requirements, questionnaires, independent attestations such as SOC 2 Type II and ISO/IEC 27001, and testing where justified.
- Contracts should cover incident notification, audit rights, vulnerability handling, SBOMs, data return and deletion, subcontractors and support lifetime.
- Software escrow protects against supplier failure if deposits are current and verified.
- Customers remain responsible for configuration, access and data in acquired software and SaaS.
- Low-code platforms need inventory, environment separation, connector policies and review of critical apps.
- AI-generated code goes through the same controls as any code; AI products bring risks cataloged in the OWASP Top 10 for LLM Applications and practices in NIST SP 800-218A.
- COTS
- Commercial off-the-shelf software sold to many customers.
- SOC 2 Type II
- An independent report on the design and operating effectiveness of a service organization's controls over a period.
- Complementary user entity controls
- Controls a customer must operate for a service provider's controls to be effective.
- Software escrow
- Deposit of source code with a neutral agent for release to customers on defined events.
- Shared responsibility model
- The division of security duties between a cloud provider and its customer.
- Citizen developer
- A business user who builds applications on low-code or no-code platforms.
- Hallucinated dependency
- A non-existent package suggested by an AI assistant, which attackers may register.
- Prompt injection
- Manipulating an AI model's behavior through crafted input that overrides its instructions.
Practice problems
Work each problem on paper first, then reveal the answer to check.
Does buying SaaS transfer accountability for customer data?
Show answer
No; the organization remains accountable to regulators and customers.
When should security requirements enter an acquisition?
Show answer
When requirements are first written, before products are selected.
What does a SOC 2 Type II report describe?
Show answer
The operating effectiveness of a service organization's controls over a period, tested by an independent auditor.
What should a reader check in a SOC 2 report?
Show answer
Scope, period, exceptions and complementary user entity controls.
Name four security terms for a software contract.
Show answer
Incident notification, audit rights, vulnerability fix times, SBOMs, data return and deletion, subcontractor limits, support lifetime.
When is software escrow useful?
Show answer
When the deposit is current and verified and the customer can maintain the code if it is released.
Who secures a SaaS tenant's configuration?
Show answer
The customer.
Give two governance controls for low-code platforms.
Show answer
Application inventory, environment separation, connector restrictions, review of critical apps, training.
Why are hallucinated dependencies a risk?
Show answer
Attackers can publish malicious packages under the suggested names.
Who owns AI-generated code once merged?
Show answer
The developer who merged it, under the organization's normal accountability.
Lesson quiz · 5 questions
Score 60% or more to complete this lesson.
Create a free account to save your progress, take quizzes and earn a certificate.